

Most organisations install PIM and still keep standing privilege in place. In one 2024/2025 practitioner study, the average identity with Global Administrator rights activated that role 5.5 of 30 days, while the top half averaged about 15 of 30 days. That's not just-in-time control, that's overuse with a Microsoft licence attached.
If you're running a Microsoft tenant in Saskatchewan, Alberta, or Ontario, that's the key question, not whether PIM is turned on. The question is whether your setup removes permanent admin exposure, holds up under audit, and doesn't break operations when your team needs to work.
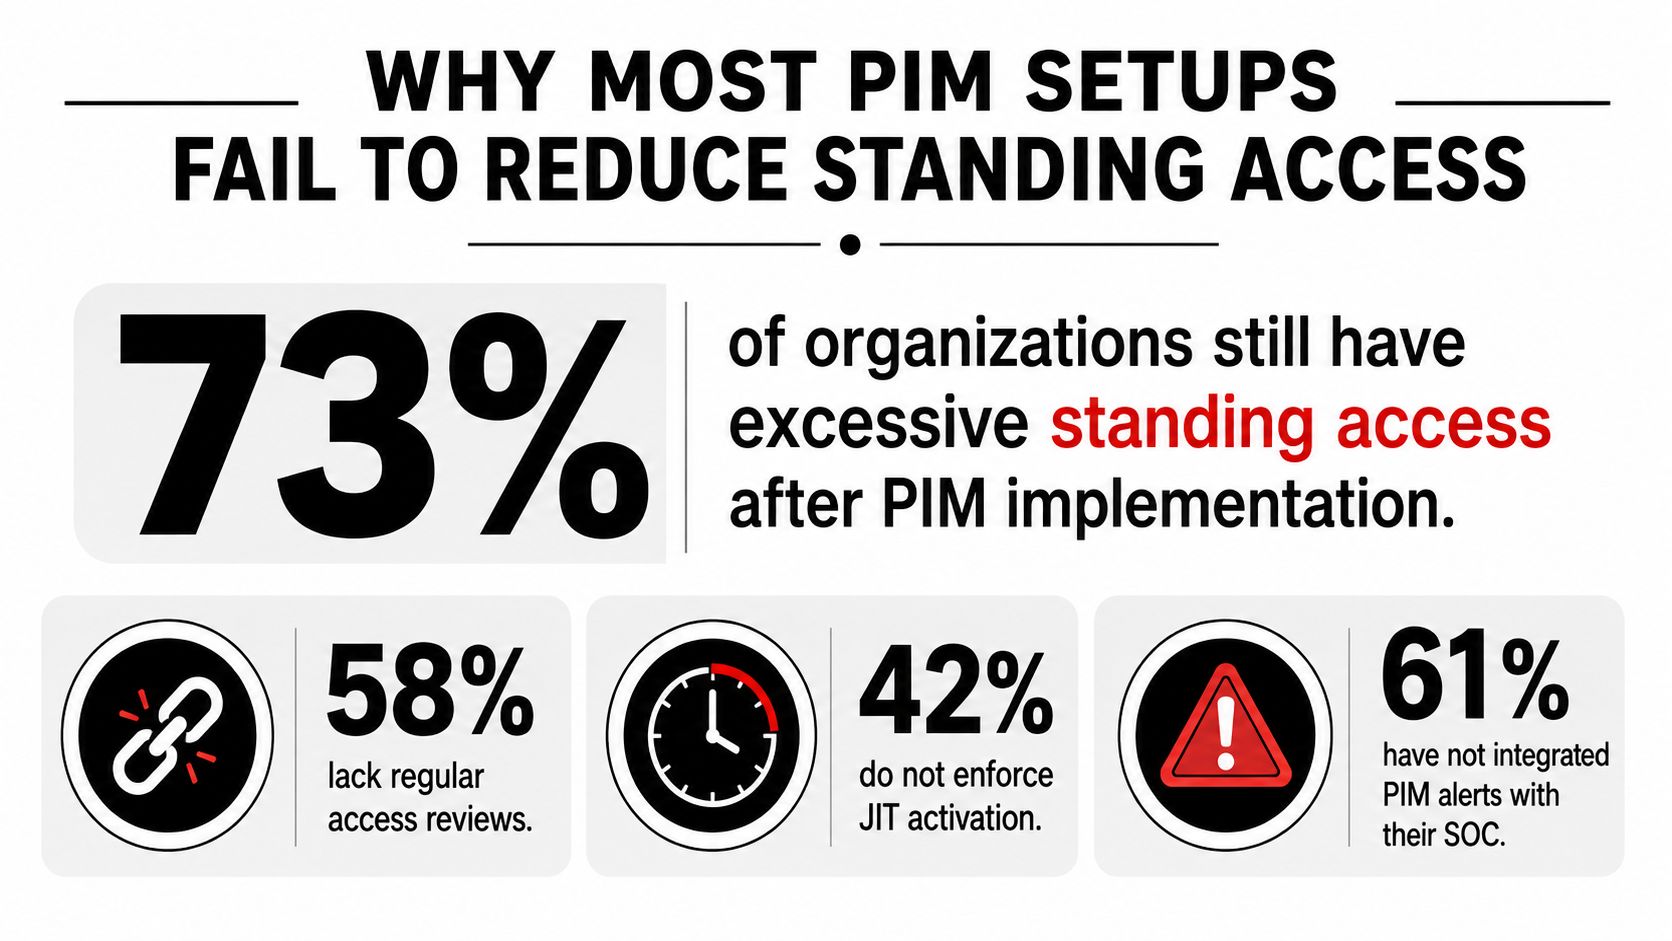
Why Most PIM Setups Fail to Reduce Standing Access
The biggest mistake I see is treating Privileged Identity Management as a switch. Teams buy the licence, turn on a few role settings, and assume the tenant is safer. In practice, many deployments drift into a soft version of standing access because nobody does the discovery work that shows who still holds permanent privilege and why.
That matters in regulated Canadian environments. Auditors and insurers do not care that the feature exists, they care whether standing privileged access went down and whether you can prove it. Microsoft's own PIM guidance positions the service as a way to manage, control, and monitor access to important resources, but that only works when permanent admin rights are replaced with eligible assignments and then activated only when needed.
Practical rule: If privileged roles are getting activated almost every business day, the rollout has not changed behaviour enough.
Practitioner studies show the same failure pattern. Many organisations keep privileged roles active far more often than intended, which means eligibility exists on paper while real exposure stays high. For Canadian SMBs, that is the failure mode that creates ugly audit questions later.
Start with discovery, not policy
A proper privileged identity management (PIM) setup starts before the first setting is touched. Inventory every standing global and privileged admin account, map role boundaries, and identify emergency break-glass accounts you will keep outside policy. If you skip that, you end up protecting the wrong accounts and leaving the primary attack paths intact.
My rule on SMB rollouts: if you cannot name every account that can become Global Administrator, you are not ready to configure PIM.
The right discovery phase also exposes who needs standing access. Some users belong in eligible assignments with short activations, and some roles are misclassified entirely. That distinction is what separates a defensible rollout from a checkbox exercise.
Prerequisites and Tenant Discovery Before PIM Configuration
PIM has a licensing gate, and Canadian SMBs need to respect it before planning timelines or controls. Microsoft Q&A states that the directory must have one of these paid or trial licences to use PIM, Azure AD Premium P2, Enterprise Mobility + Security E5, or Microsoft 365 M5, and the person configuring it must be Global Administrator or Privileged Role Administrator Microsoft Q&A on Azure PIM prerequisites. That's not a minor detail, because it affects who can do the work and whether the feature is even available in the tenant.
Check the tenant before you touch role settings
Start with a hard inventory of current privilege. List every global administrator, privileged role administrator, security administrator, and any resource-level owner or contributor assignments that matter to production. Then map service principal dependencies and shared administration patterns, because those often hold hidden access paths that a clean-looking PIM dashboard won't catch.
Break-glass accounts need special treatment. Keep them cloud-only, permanently assigned, and excluded from PIM and Conditional Access policies so you don't lock yourself out during tenant-wide MFA failures or authentication incidents. I've seen teams create a beautiful policy set and then trap themselves behind it.
Separate Tier 0 from Tier 1
Use a simple boundary: Tier 0 for infrastructure and global roles, Tier 1 for app and helpdesk roles. Don't let those blur together during configuration, because the controls should not be identical. The more sensitive the role, the more opinionated the activation process should be.
Don't build policy around your org chart. Build it around blast radius.
| License Tier | Key Inclusions | Typical SMB Fit |
|---|---|---|
| Azure AD Premium P2 | PIM capability for eligible privileged access | Best fit when the tenant already needs identity governance controls |
| Enterprise Mobility + Security E5 | PIM capability in a broader security bundle | Better for organisations already standardised on Microsoft security licences |
| Microsoft 365 M5 | PIM capability inside the Microsoft 365 stack | Useful where licensing is already consolidated for premium users |
For Canadian SMBs, that table usually resolves one practical question fast. If the licences aren't already in place, the rollout has to wait for procurement or be narrowed to the users who need privileged workflows.
Configuring PIM Role Settings and Approval Workflows
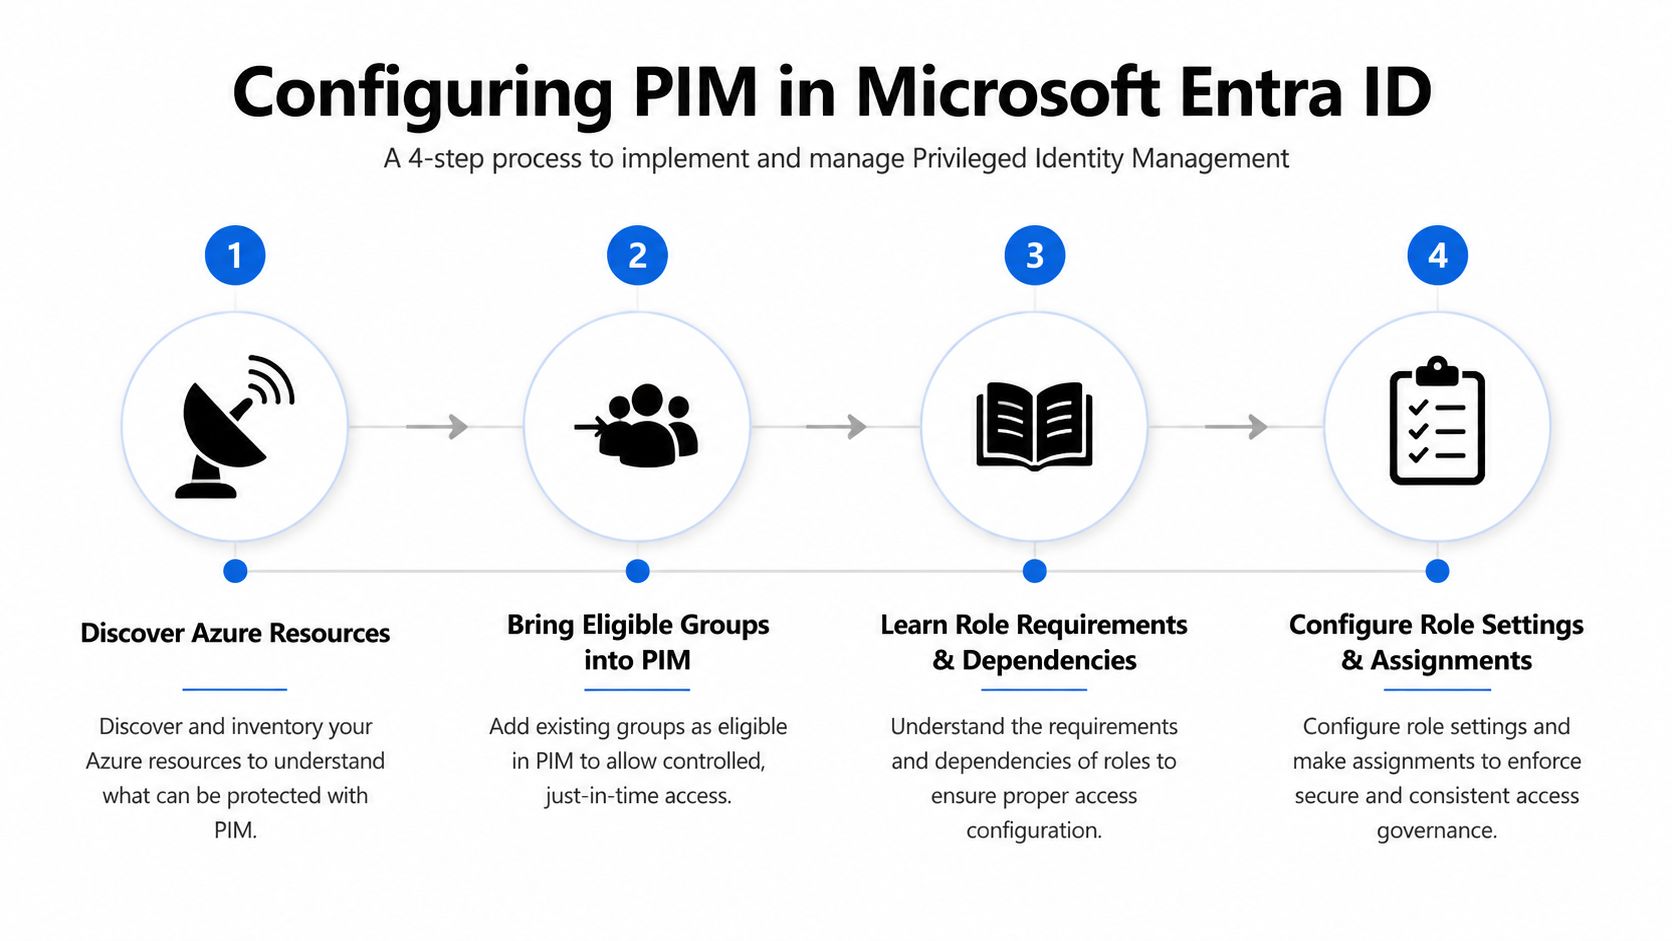
Microsoft's deployment sequence is more disciplined than many admins expect. The practical order is discover Azure resources, bring groups into PIM, learn role settings for Entra ID roles and Azure resource roles, enable group settings, assign roles, then activate, approve, extend, and finally run access reviews Microsoft Entra privileged identities deployment guide. That sequence matters because it forces you to treat directory roles and cloud resource roles as separate governance problems. It also keeps you from rushing into approval workflows before you've mapped what needs privileged access.
Configure the role, not just the user
Microsoft Entra roles and Azure resource roles are different controls. Directory administration sits in one control plane, resource administration sits in another, and PIM documentation separates them for a reason Microsoft Entra PIM overview. If you apply one policy to both, you leave gaps.
For high-risk roles, convert standing assignments into eligible assignments, then apply activation controls. Use MFA, require justification, and set a short activation window. The Microsoft deployment guide also allows compliant devices or specific authentication strengths for privileged access, which is the right move when you are hardening a tenant for regulated work Microsoft Entra privileged identities deployment guide. That gives you tighter control without turning every request into a manual exception.
Keep approval logic simple where it should be simple
Tier 1 support access does not need a bureaucratic maze. MFA-verified self-activation with justification is usually enough for everyday support roles. When you over-engineer approvals, admins start looking for bypasses, and then the control becomes theatre.
Use approval where the risk justifies the delay. If every ticket needs two humans and a ceremony, the business will fight the control.
For more sensitive roles, especially Global Administrator and high-impact resource owners, approval makes sense. The point is to match friction to risk, not to make the workflow painful for its own sake. That is how you get compliance without wrecking operations.
Just-in-Time Activation with MFA and Conditional Access
The cleanest PIM setup blocks the bad path before anyone gets elevation. That means just-in-time activation tied to MFA and Conditional Access, not PIM sitting on its own. If your tenant still gives out active admin access by default, you have not reduced the attack surface enough.
A real compromise scenario makes that plain. A helpdesk admin credential gets used by an outside actor after hours, and the attacker tries to move up to Global Administrator. If standing privilege has been removed, there is no live cloud role to steal. The attacker has to request activation, pass MFA, and, in a tighter setup, clear approval first.
Build the activation path to fail closed
The activation flow should do three things well. It should force MFA at activation, check device and session posture through Conditional Access, and send alerting into your monitoring stack the moment something abnormal happens.
That alerting is what turns PIM from policy into control. In one compromise assessment scenario, an attempted activation triggered an instant alert in Sentinel and Log Analytics, which let the team isolate the account and revoke active sessions before privilege escalation finished. That is the point of coupling PIM with monitoring. The control should not only approve access, it should watch for misuse and surface it fast enough to matter.
The Microsoft Entra privileged identities deployment guide also supports on-demand administrative use, approval-based just-in-time activation, and role activation requirements tied to compliant devices or authentication strengths. That is the right model for Canadian SMBs handling regulated data, because it gives you temporary elevation and a trail you can defend later.
Don't make legitimate work harder than it needs to be
Use time-of-day restrictions carefully. They help reduce odd-hour activations, but they should not block legitimate after-hours maintenance if your operations team works that way. The policy should stop abuse, not punish the people keeping production alive.
If your Conditional Access and PIM settings are aligned, the attacker hits a wall. If they are not, they will keep finding the easiest path.
Alerting, Auditing, and PIPEDA Compliance Readiness
A PIM rollout without audit retention is a temporary convenience, nothing more. Canadian organisations need logs that show who activated access, who approved it, and when the role ended. Microsoft's deployment guidance supports access reviews and role lifecycle management, but the compliance value comes from keeping evidence in a form auditors can use.
Route the right events to the right place
Send activation events, approval decisions, and role assignment changes into Azure Sentinel or Log Analytics for long-term retention. Standard logs should also go to long-term storage such as Azure Blob or Sentinel when your retention and audit windows require it. If those records live only in the default portal history, you will be exposed the first time someone asks for proof.
The operational problem is usually not logging itself. It is governance around approvers. High-impact roles need clear primary and secondary approvers, and those approvers must not create segregation-of-duties problems by approving their own access or approving roles they also administer.
Use the logs to prove behaviour changed
You need to show whether standing privilege declined and whether time-bound activation is doing the work. The practical KPI is straightforward, compare the decrease in standing privileged hours with the number of legitimate activations, then review the pattern during audit cycles. In a well-run environment, that evidence supports both security review and compliance review without drama.
If you cannot show who activated access, why they activated it, and when it expired, you are not ready for a serious PIPEDA review.
For Canadian SMBs, PIPEDA-aligned justification logging is the standard to aim for. The logs should tell the story clearly enough that a reviewer can follow the chain from request to approval to expiry without hand-waving. That is what makes the deployment defensible.
Pilot Phase and Full Go-Live Rollout Strategy
A PIM rollout should not go live across the tenant in one shot. The cleaner delivery pattern is to treat it as a staged change, with discovery and scoping first, then policy design and staging, then a pilot with user training, and only after that the full cutover from standing access to controlled activation. That order matters because each phase exposes a different failure mode before it turns into an outage or an audit mess.
A good Saskatchewan pilot doesn't try to impress anyone
In a typical Saskatchewan SMB rollout, I start with IT leadership and a small Tier 1 pilot group. They activate eligible roles in the browser, test the PowerShell path where needed, and work through the approval flow before anyone else does. That surfaces the ugly parts early, especially approver availability, notification routing, and whether the workflow is usable under pressure.
The delays are usually predictable. PIPEDA-aligned justification logging takes time, and so does agreeing on who can act as primary and secondary approvers for high-impact roles without creating segregation-of-duties problems. Those are governance calls, not software settings, and management needs to make them before the rollout spreads.
Cut over standing access in one deliberate move
The last step is to move all global roles from permanent eligible or active status to time-bound eligible assignments with strict activation windows. Do not leave “temporary” access sitting active because the team is busy. That just rebuilds the old standing-access problem under a new label.
If a configuration change disrupts business operations, roll it back cleanly and fix the policy design before trying again. I would rather see a controlled rollback than a rushed cutover that leaves admins frustrated and the tenant only half protected.
Operational SOPs and Troubleshooting Common PIM Issues
The two failures that do the most damage are preventable. One is locking yourself out by leaving emergency cloud-only break-glass accounts inside PIM and Conditional Access. The other is turning routine support access into a paperwork maze, which pushes admins toward workarounds instead of compliant activation.
Build your SOP around the failure modes
Your standard operating procedure should spell out role activation, emergency recovery, and access reviews in plain language. Do not bury the steps in a policy binder nobody opens. The person handling a live incident needs to know exactly what to click, who can approve, and what to do if PIM itself is the blocker.
- Role activation procedure: Define who can request access, what justification they must provide, and which roles need approval before activation.
- Break-glass recovery path: Keep emergency accounts outside PIM, store credentials securely, and document who can use them during lockout scenarios.
- Access review cadence: Review eligible assignments on a regular schedule and remove users who no longer need privileged access.
- Approval routing: Send notifications to named approvers who watch the queue, not a shared mailbox that gets ignored.
Don't ignore non-human identities
PIM guidance often centres on human administrators, but privileged access programs also need controls for service accounts, integration accounts, and shared admin accounts. Those identities carry secrets, ownership, and rotation needs that PIM alone does not solve. If you leave them untouched, you have kept a major attack path open.
That matters in Canada because compromised valid accounts are one of the top ransomware entry paths identified by the Canadian Centre for Cyber Security in its incident assessment. A rollout that protects human admin roles while ignoring workload and shared identities is incomplete, and it does not give you a clean PIPEDA story either.
Operational truth: the best PIM policy is the one your team can actually follow at 2 a.m.
For some organisations, outside help can be useful. Accelerate IT Services Inc. provides identity and access management services that include privileged controls and governance and access provisioning, which can support a PIM rollout without forcing the internal team to invent every process from scratch.
Answer the questions admins always ask
A typical PIM deployment usually lands in the 4 to 6 week range when discovery, policy design, pilot training, and cutover are done properly. A locked-out break-glass account should never sit inside the same control path as day-to-day admins, because that defeats its purpose. PIM also does not satisfy PIPEDA by itself, it supports the audit trail, but you still need retention, approver governance, and documented procedures. For service account rotation, treat it as a separate control stream with ownership and secret management, not as a normal user activation problem.
Review the failures first, then tune the workflow. That is how you keep privileged access usable without giving up control.


