
Most advice about managed IT services Brampton is too soft. If a provider only resets passwords, closes tickets, and calls that “managed”, you're not buying resilience, you're buying expensive break-fix with a monthly invoice.
That distinction matters because Brampton is already a mature managed services market, not a fringe one. Buyers can compare dedicated city listings on Clutch, and regional pricing guides commonly land around $100 to $200 per user per month depending on scope, device count, and cybersecurity requirements, which tells you the market has standardised around recurring service delivery, not random hourly support (Clutch's Brampton MSP directory).
Why Most Brampton IT Providers Are Not True Managed Services
A lot of local providers still sell reactive IT support and label it as managed services. That creates a real risk for Brampton businesses, because a true managed service provider is supposed to maintain, monitor, and secure your environment on an ongoing basis with fixed pricing and proactive control, managed IT services definition and fixed proactive model.
The difference shows up in the contract, the tooling, and the operating model. A real MSP owns monitoring, patching, backup oversight, and security escalation. A break-fix shop sells time, while a true MSP is on the hook for the health of the environment.
Practical rule: if the provider's main promise is “call us when something breaks”, you are still running on break-fix. Managed services should cut the number of breaks you ever see.
What a real MSP controls
A proper partner does more than answer the helpdesk. It watches the environment, standardises it, and closes the gaps that create repeat incidents. That includes identity, endpoints, network devices, cloud services, and recovery planning, because weak control in any one of those areas turns into a security or downtime issue.
If you are comparing vendors, ask whether they coordinate these areas as one operating model:
- Continuous monitoring, not occasional check-ins.
- Patching discipline, not vague “maintenance”.
- Security ownership, not just antivirus.
- Backup oversight, not a hope-and-pray backup job.
- Cloud administration, not “we support Microsoft 365 when it breaks”.
For a plain-English definition you can use internally, see what a managed IT services provider does. If your team is spread between office and home, pressure-test providers against reliable internet providers for remote workers, because weak connectivity still becomes an MSP problem when users cannot reach core systems.
The core question is simple. Are they lowering risk every month, or only reacting after users complain? If they cannot explain that clearly, they are a support queue with a monthly retainer, not a managed services partner.
The Core Service Stack Every Brampton MSP Should Deliver
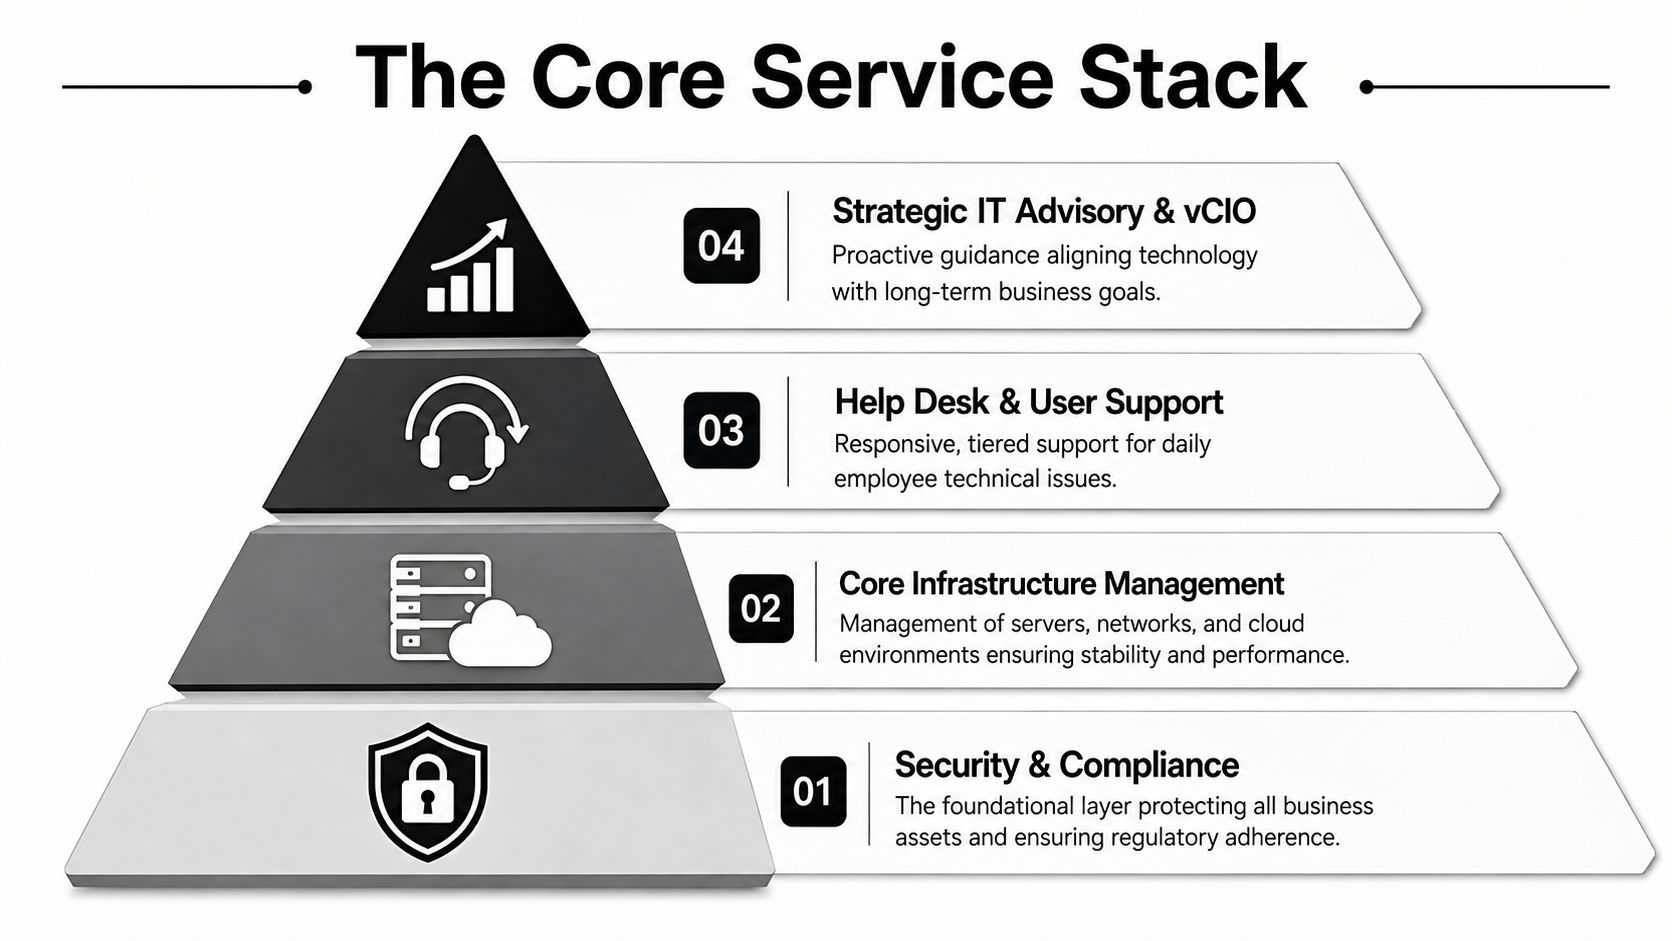
A serious managed IT services Brampton provider should build its service stack from the bottom up. If one of these layers is missing, the whole arrangement is weaker than it looks on paper. Brampton-area service pages consistently bundle 24/7 monitoring, endpoint protection or MDR, firewall management, Microsoft 365 administration, and backup and disaster recovery, which is the right direction for an always-on operating model (Brampton managed IT service area examples).
Security and recovery come first
The foundation is Security and Compliance. That means endpoint protection, vulnerability management, backup integrity, and documented recovery. If the provider doesn't actively protect data and prove it can restore systems, the rest is window dressing.
Infrastructure keeps the business moving
Above that sits Core Infrastructure Management, which covers servers, network gear, Wi-Fi, cloud environments, and the firewall stack. In practical terms, this prevents outages, not just explains them after the fact.
Users still need real support
Helpdesk matters, but it should be tiered and tied to the rest of the stack. Fast ticket closure is useful. It's not enough on its own if identity, cloud, and endpoint controls are weak.
Advisory prevents drift
The top layer is strategic guidance. That's where the MSP helps you choose lifecycle timing, standardise the tenant, and avoid random technology purchases that create more risk than value. For remote-heavy teams, a useful companion resource is reliable internet providers for remote workers, because network stability outside the office affects how well managed support performs.
Use patching best practices for ConnectWise RMM as a reference point if you want to pressure-test a provider's maintenance discipline. If they can't explain their patch workflow clearly, don't assume they have one.
Identity Governance and Zero Trust: The Key Differentiator
The biggest gap in commodity MSPs is usually identity. Firewalls still matter, but they are no longer the main boundary. Microsoft Entra ID, Conditional Access, phishing-resistant MFA, and Privileged Identity Management are the controls that stop stolen credentials from turning into a business incident. Zero Trust should be the default posture, not an add-on.
The Ontario compliance context makes this even more important. Brampton businesses handling personal information need to think about PIPEDA, and some sectors also need to account for PHIPA and workplace privacy obligations tied to Ontario's Working for Workers Act. Canadian privacy guidance also puts real weight on accountability, transfers, and safeguarding personal data, so your MSP should explain how access, logs, retention, and backups are controlled. If a provider cannot describe that plainly, they are not managing risk, they are just selling support.
What to demand in the tenant
A vendor that cannot explain tenant hardening in plain terms is already behind. Ask how they handle:
- Standing admin rights, because those should be rare.
- Break-glass access, because emergency access needs to exist without becoming a backdoor.
- Audit logging, because compliance without logs is just a story.
- Conditional Access, because legacy sign-in paths are still a common failure point.
- Data residency, because many Brampton buyers need Canadian datacentres for Microsoft 365 and Azure workloads.
If you want a practical reference point for identity control, use the 2026 IAM guide. If the MSP treats identity governance as optional, they are behind the market.
Direct advice: do not buy “security” from a provider who still talks mostly about the firewall. Identity is where modern compromise starts, and it is where your control has to begin.
For broader context on the network side, network security for small businesses is a useful external primer, but your real decision point is whether the MSP can translate those ideas into a hardened Microsoft 365 tenant and documented access policy.
Understanding Brampton Managed IT Pricing and Value Tiers
Brampton pricing is easy to read if you know what you are buying. Regional directories put managed IT support around $100 to $200 per user per month, depending on scope, device count, and cybersecurity requirements. That range is useful because it shows managed IT is not a mystery service. You are choosing how much control, security, and accountability you want inside a fixed monthly model. For a broader market comparison, the managed IT services UK guide shows the same buying logic, scope drives price, not the sales pitch.
The mistake is chasing the lowest quote and ignoring what got stripped out. A cheap plan can become expensive quickly if it leaves out controls your insurer expects or skips recovery testing. That gap is where many Brampton owners get hurt, because the invoice stays low while the risk sits off the books.
Brampton Managed IT Service Tiers
| Price Tier | Core Services | Security Features | Compliance Support |
|---|---|---|---|
| Entry | Helpdesk, basic remote support, limited monitoring | Basic endpoint protection, simple patching | Light documentation, minimal audit support |
| Standard | 24/7 monitoring, Microsoft 365 administration, backup oversight | Endpoint protection, firewall management, recovery testing | Better logging, clearer control evidence |
| Advanced | Full NOC coverage, managed detection and response, cloud backup, disaster recovery | Stronger identity controls, MFA hardening, privileged access discipline | Audit-ready records, stronger insurer support |
Use the table as a budget filter, not as a shopping list. The entry tier may work for a very small office with limited exposure, but it should not be sold as full managed services. If a provider markets itself as an MSP while giving you thin monitoring and weak recovery support, the mismatch is a sign to keep looking.
The core pricing question is whether the provider is managing risk or just handling tickets. Brampton businesses with cyber-insurance requirements, Canadian data residency concerns, and Microsoft 365 access issues need more than break-fix support. They need documented controls, clear recovery procedures, and identity governance that stands up when something goes wrong.
The Evaluation Checklist and Questions That Reveal Provider Quality
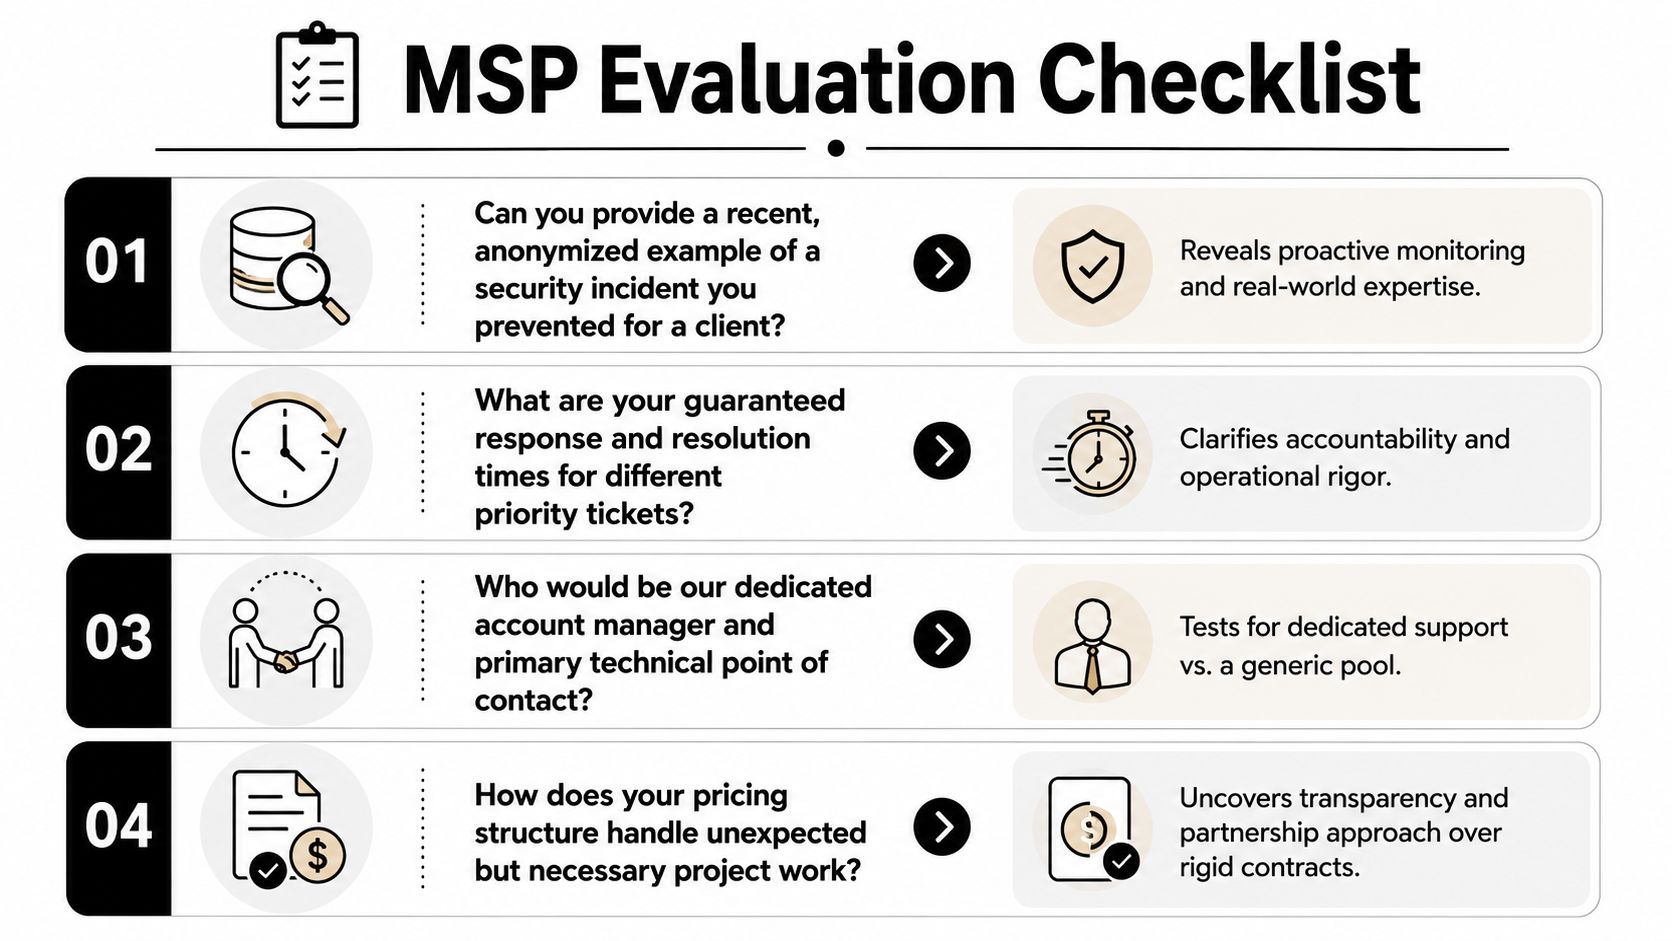
Ask harder questions than “do you offer support?” If the provider can't answer them cleanly, they're not ready for a business that cares about uptime, auditability, or cyber-insurance friction. The strongest Ontario service commitments I've seen are measurable, including 99.9% guaranteed SLA uptime, under 15 minutes average response time for priority tickets, and 24/7/365 helpdesk and monitoring coverage (GTA managed services commitments).
Questions that separate operators from order-takers
Can you show how you prevent incidents, not just resolve them?
A good answer includes monitoring, alert triage, and the security controls used to stop repeat issues.How do you handle ransomware readiness and insurance evidence?
You want to hear about immutable backups, incident reporting, restore testing, and documented controls.Who owns escalation when something serious happens?
If the answer is “the helpdesk”, keep looking. Serious incidents need named ownership.What will you document for an audit or claim?
The right provider can support audits without creating extra operational drag.
If the vendor dodges backup validation or says recovery is “covered” without testing, assume it isn't covered.
A decent MSP should also be able to explain tabletop exercises, recovery time objectives, and how it handles privilege reviews. Those are the details that matter after an incident, not the glossy proposal language.
How Proper Onboarding Eliminates Downtime and Security Gaps
A Brampton logistics and distribution firm is a good model for this kind of work. It was dealing with recurring network outages and server crashes tied to ageing perimeter hardware and unmanaged switches. The business was losing nearly 12 to 15 hours of unbudgeted downtime per month during peak shipping periods, which is exactly the kind of problem that looks “technical” on the surface but is really an operational risk issue.
The fix was a structured overhaul. Redundant firewalls went in, managed network switches replaced the unmanaged gear, and local identity moved to Microsoft Entra ID with standardised Conditional Access policies. After proactive NOC monitoring and automated threat containment were in place, downtime fell by over 95% (Brampton operational support example).
What good onboarding looks like
Identity and infrastructure audit
Map users, endpoints, cloud tenants, and line-of-business apps before touching anything. That gives the provider a baseline for access, device trust, and data exposure.Security and privilege hardening
Remove standing admin access, enforce MFA, and define emergency access properly. Cyber-insurance readiness starts with control over privilege and recovery.Network and firewall standardisation
Replace inconsistent gear, segment traffic, and shut down legacy auth paths. Brampton businesses with hybrid users and Canadian data residency concerns need that discipline before they expand cloud use.Backup and disaster recovery validation
Test immutable backup streams and prove restore works before you need it. A backup that has never been restored is a liability, not protection.Staff onboarding and security awareness
Train people on ticket flow, passwordless sign-in, and phishing resilience. Identity governance fails fast when users do not understand how access requests, approvals, and sign-in changes work.
For a live example of structured MSP delivery, the managed IT onboarding video is useful because it shows how phased change reduces disruption when the environment is already unstable.
Shallow onboarding leaves the provider guessing. Disciplined onboarding is engineering.
Making the Decision and Securing Your Infrastructure
Brampton's managed services market is deep enough that buyers can be selective. Clutch's city-level MSP listings show real local demand, while IDC describes Canadian managed services as being in a slow growth phase with consolidation among providers (IDC Canadian market shares report). That combination usually favours providers with stronger security, compliance, and operational depth over small shops that only do ad hoc support.
My recommendation is simple. Choose the MSP that can prove three things without hand-waving. It can control identity, it can recover systems, and it can document everything that matters for compliance and cyber-insurance. If a provider cannot speak clearly about Canadian data residency, audit logs, conditional access, or recovery validation, it's not ready for a regulated Ontario SMB.
The right partner should feel like an extension of your risk management function, not a ticket desk. That's the standard Brampton businesses should hold.
Secure Your Corporate Identity & Infrastructure
Managing access risks and maintaining platform compliance is the foundation of operational resilience for Canadian SMBs. Don't wait for a compliance audit or a security event to find hidden vulnerabilities in your cloud tenants.
Take a proactive step to protect your business operations:
- Request a Local Audit: Secure an IT infrastructure and identity security review customized for your specific environment.
- Get Started Today: Access our Identity Security Assessment Framework.


