
You've probably seen this play out already. A simple password reset lands in the queue, someone approves it too quickly, and a few hours later the actual problem shows up in Microsoft 365, OneDrive, and a file share tied to a regulated client workflow. That's the point where managed IT service solutions stop being a helpdesk purchase and start being an operational risk decision.
For Canadian SMBs in Regina, Saskatoon, Moose Jaw, Calgary, and Toronto, the market has already shifted that way. In North America, managed services held 33.0% of global managed services revenue in one 2025 estimate, cloud deployment held 52.35% of revenue, hybrid cloud is projected to grow at 11.92% CAGR through 2031, and managed infrastructure services held 38.40% of 2025 revenue, which tells you the basic operating model is now a layered mix of cloud, on-prem, identity, and security work (Grand View Research). The practical takeaway is blunt. If your current provider still sells “support” as a loose bucket of tickets, you're buying yesterday's model.
When a Password Reset Becomes a Board-Level Problem
A password reset looks harmless until it isn't. In a real Saskatchewan SMB environment, a single compromised account can touch Microsoft 365, synced files, shared inboxes, and a client system that nobody remembered was still exposed to broad permissions. That's why executives need a stronger definition of managed IT service solutions than “outsourced support.”
What Managed IT really includes
A serious managed contract is a recurring operating model, not a one-off fix. The usual layers are helpdesk and end-user support, a 24/7 network operations centre, endpoint protection and patch management, cloud enablement for Microsoft 365, Azure, or Google Workspace, backup and disaster recovery, and identity and access management with conditional access and lifecycle workflows. That last layer is the one buyers often underweight, even though it determines whether a stolen password becomes a contained nuisance or a lateral movement event.
Practical rule: If your provider can't explain how identity, endpoint, backup, and cloud controls connect, they're selling parts, not resilience.
What sits at the edge of the contract matters too. Hardware procurement, major migrations, and large project work usually belong in separate statements of work, not buried in a flat monthly fee. That distinction matters because a good managed service should be predictable in operations, but not vague about scope.
How to read the contract like an operator
Use this simple table to separate core coverage from nice-to-have extras.
| Layer | What it delivers | Business question it answers |
|---|---|---|
| Helpdesk | User support, ticket intake, escalation | Who handles routine issues without derailing internal staff? |
| NOC | Monitoring of network, server, and cloud health | Who notices a problem before users do? |
| Endpoint security | Protection, patching, alerting | How fast do you close the easy attack paths? |
| Cloud enablement | Tenant setup, admin support, change control | Who keeps Microsoft 365 or Azure from drifting into chaos? |
| Backup and recovery | Backups, restore tests, documented recovery steps | Can you actually recover data, not just store it? |
| Identity and access | MFA, Conditional Access, lifecycle workflows, least privilege | Who controls who gets in, and who gets removed on time? |
The managed services model is mainstream in North America, not fringe outsourcing, and the cloud-first mix makes that obvious (Grand View Research). For a practical resource on hardening access, the guide on secure identity-free systems with Ciphar is a useful read if you want another perspective on reducing brute-force exposure without relying on guesswork (Ciphar). The point isn't the brand. It's the discipline. Identity has to sit at the centre of the service stack.
Helpdesk, NOC, and the Identity Layer That Ties Them Together
Most buyers separate helpdesk, monitoring, and identity into different mental boxes. That's a mistake. A good helpdesk is also a signal source, because repeated lockouts, MFA fatigue, and strange mailbox behaviour are often the first clues that an account has been probed or abused.
Helpdesk is where the pattern shows up
If your ticket queue keeps filling with login failures, mailbox access complaints, or device enrolment issues, you don't have a “user problem.” You have an identity or endpoint control problem. That's why the helpdesk needs tight escalation paths into security operations, not just polite scripts and password resets.
The same logic applies to the NOC, the layer that watches network, server, and cloud health around the clock. If the NOC spots unusual authentication behaviour, failed backups, or service degradation early, it reduces the window in which a small issue turns into downtime. If it only reacts after users complain, it's not operating as a proactive control layer.
For a plain-English overview of what a NOC does in a managed environment, this explainer is worth keeping handy: what a NOC is in managed services.
Identity policy is the control point
In Canadian guidance for managed IT services, the strongest posture is a default-deny identity layer built on MFA, Conditional Access, and least-privilege administration. That makes sense because compromised credentials remain a leading attack path, and policy is what stops one breach from becoming lateral movement across Microsoft 365, cloud apps, and remote endpoints. For SMBs in Calgary, Regina, Saskatoon, and Toronto, this is not a theoretical best practice. It's the control plane that makes remote work and shared systems survivable.
For privacy and compliance, the risks are significant. The Office of the Privacy Commissioner of Canada says PIPEDA applies to private-sector organizations engaged in commercial activities, and its core obligations include limiting collection, using appropriate safeguards, and retaining personal information only as long as needed for the identified purpose (KPMG summary of Canadian privacy obligations). That means identity reviews, access removal, and audit trails are part of the compliance conversation, not just IT housekeeping.
A password reset is rarely the root issue. It's usually the first visible symptom of a weak access model.
Endpoint Protection, Cloud Enablement, and Backup That Actually Recovers
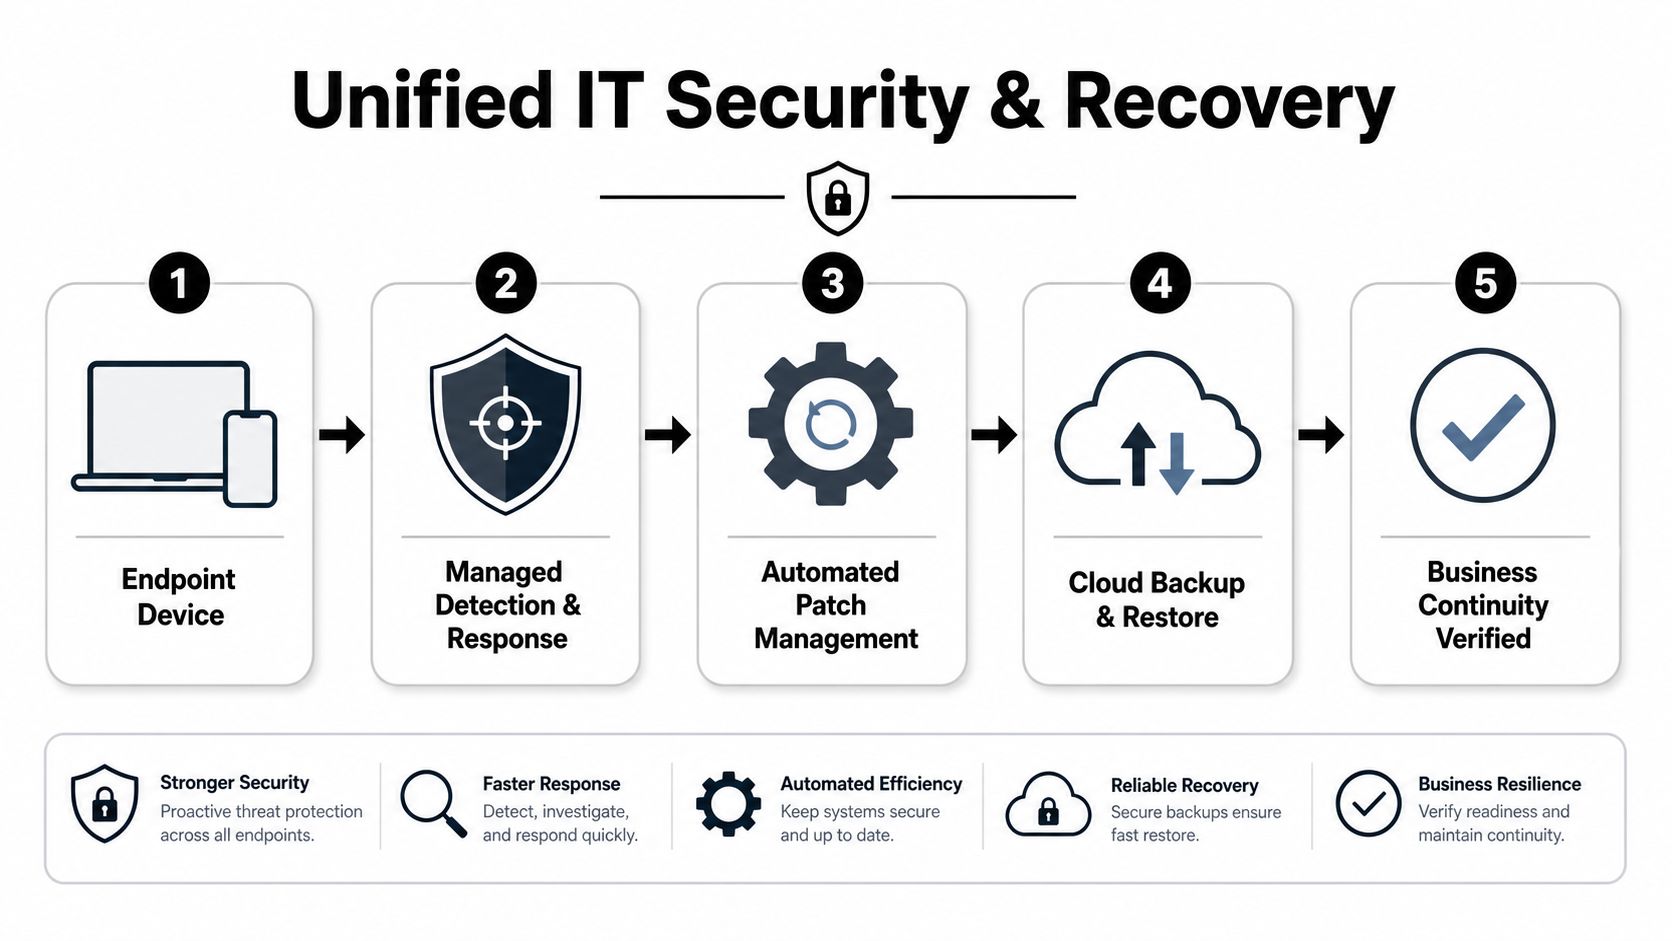
Security tools sold separately often create the illusion of coverage. The better managed stack bundles endpoint protection, patching, monitoring, and recovery because those layers depend on each other in actuality. If one breaks, the rest has to absorb the damage.
The endpoint layer has to move fast
A managed endpoint program should include protection, patch management, and a clear response path when malware, theft, or credential abuse shows up. The reason is simple. Vulnerabilities stay exposed for less time, compromise is detected sooner, and the cleanup process is less chaotic when the provider owns both monitoring and remediation. A firewall alone won't save you if laptops sit unpatched and unmanaged.
Cloud administration is not the same as cloud hosting
Microsoft 365 and Azure need ongoing governance, not just onboarding. Tenant configuration, audit logging, permission cleanup, and shadow IT control are the difference between a useful cloud estate and a sprawl of orphaned access. If your MSP says they “support Microsoft 365” but doesn't mention access reviews, admin role control, or lifecycle workflows, they're talking about user tickets, not cloud enablement.
Backup and disaster recovery deserve the same honesty. A backup that has never been tested is a hope, not a control. A solid service package uses documented BCDR processes, restore-point testing, and clear recovery ownership so the business can get back up instead of arguing about what was preserved.
The recovery piece matters for privacy too. Canadian privacy frameworks don't let organizations keep personal data indefinitely and call that safe. Retention, access control, and recoverability have to line up with the purpose of the data and the safeguards around it (KPMG summary of Canadian privacy obligations).
For a deeper look at recovery planning, this overview of disaster recovery in a managed environment is a sensible companion read.
Business Benefits and ROI in Language Your Board Will Read
Boards don't care about service catalogues. They care about whether the business stays operational, stays compliant, and avoids expensive surprises. That's the case for managed IT service solutions, especially when the provider can prove the work with reporting.
What the board should measure
Every layer should map to an outcome the board understands.
- Helpdesk and NOC: shorter time to detect and resolve incidents.
- Identity governance: fewer unauthorized access events and cleaner offboarding.
- Patch and endpoint management: lower exposure from known vulnerabilities.
- Backup and recovery: faster restoration and less data loss when something fails.
- Cloud administration: fewer configuration mistakes and less drift.
- Compliance alignment: fewer audit findings and cleaner evidence collection.
That's where the monthly fee stops looking like a cost centre and starts looking like operating capacity. You're not just paying for tickets. You're paying for repeatable execution, documented controls, and a team that can absorb routine demand without forcing your internal staff into constant firefighting.
If you need a model for turning operational discipline into something finance and operations can follow, this piece on how to turn your business into a well-oiled machine is a useful framing tool. The board version is simpler, though. Predictability beats heroics every time.
A fixed monthly fee is worth paying only if the provider reports on service levels, access hygiene, backup success, and incident handling. If they can't show that, the fee is just an invoice with nicer branding.
Pricing Models and SLAs That Change the Final Bill
Pricing transparency remains the most significant gap in managed services, especially for Western Canadian SMBs comparing a fixed-fee MSP with a junior in-house hire. The monthly sticker price rarely tells the whole story, because the total cost depends on onboarding, support hours, licensing, security add-ons, and project work.
The four pricing models buyers actually see
| Pricing model | Best fit | Common hidden costs |
|---|---|---|
| Per user | Office-based SMBs with predictable staff counts | Onboarding, after-hours support, Microsoft 365 pass-through, security extras |
| Per device | Mixed fleets with many endpoints | Device sprawl, mobile support, backup scope, patch exceptions |
| Tiered bundled | Firms that want an all-in support package | Limits on response scope, backup retention, MDR add-ons, escalation fees |
| Fully custom | Regulated or complex environments | Discovery work, migration projects, specialized compliance tasks, excluded services |
A simple response guarantee sounds strong until you check the escalation path behind it. A 15-minute response promise only matters if the provider clearly defines who answers, how they triage, and what happens when the issue sits outside first-line support. Credits can help, but they don't fix a weak operating model.
Practical rule: Ask what happens after the response timer starts. If the answer is vague, the SLA is mostly marketing.
The question about internal staff is where the decision gets honest. A fixed-fee MSP starts to look expensive when your environment is small and low-risk, but it can become cheaper fast when you factor in after-hours coverage, backup oversight, patching discipline, and security operations. It swings back toward in-house staffing when your internal team is already mature, your environment is stable, and the provider is mostly reselling labour instead of reducing complexity.
For Saskatchewan buyers, the key issue is not whether managed services are subscription-based. It's whether the bill is transparent enough that you can tell what you're paying for, and what you're still buying separately (Synergy Technical).
Provider Evaluation Checklist Tuned to PIPEDA and HIPAA
A vendor scorecard should force answers, not marketing language. If you're comparing providers in Regina, Saskatoon, Calgary, or Toronto, use the same lens every time and make them prove their controls.
Security operations and identity
Ask whether they run incident response playbooks, security monitoring, and managed detection and response as part of the service. Then ask for their Microsoft Entra ID security review process, including Conditional Access, lifecycle workflows, and privileged access management. If they talk only about antivirus and password policies, they're behind.
Cloud, backup, and compliance
Check whether they provide Microsoft 365 baseline hardening, audit logging, tested restore points, and documented recovery objectives. For healthcare clinics and other regulated operators, ask how they support HIPAA-aligned workflows where those practices apply, and how they align with PIPEDA safeguards, access review, and breach readiness. The right answer is specific. The wrong answer is “we take security seriously.”
For a useful compliance reference tied to regional data handling, this guide on Saskatchewan HIPAA data retention policy guidelines is worth reading before you compare providers.

Commercial fit and local proof
Ask for contract exit terms, documented service levels, and references they can discuss in Regina, Saskatoon, Calgary, or Toronto. If they can't give you local proof, they may still be capable, but you should assume on-site support will be slower or subcontracted.
Good vendors answer hard questions without getting defensive. Weak vendors hide behind jargon and bundled pricing.
What Changes for SMBs in Regina, Saskatoon, and Moose Jaw
Geography still matters. A remote-only provider can be perfectly competent on Microsoft 365, identity, and endpoint support, but tight on-site response windows in Saskatchewan are a different matter. If you need someone in the building quickly, local technician coverage changes the economics immediately.
A Manitoba or Ontario provider might look fine on paper, but a Regina plant, a Saskatoon clinic, or a Moose Jaw professional office can't always wait through a chain of handoffs. For healthcare, finance, law, and manufacturing, that gap matters because the cost of downtime is operational, not theoretical.
Here's a composite example. A 40-person professional services firm in Saskatchewan moved from break-fix support to a managed contract after a privacy exposure scare exposed sloppy account handling and weak offboarding. The firm spent the first 90 days cleaning up tenant access, enforcing MFA, tightening admin roles, documenting backup checks, and moving support tickets into a monitored queue. By month 12, the firm had fewer interruptions, faster ticket handling, cleaner access reviews, and less friction during internal audit prep.
That scenario is illustrative, not a promise. Results vary by sector, staff maturity, and how messy the environment was on day one. But the pattern is consistent. The biggest gains come from identity hygiene, clearer escalation, and someone taking ownership of the boring work before it becomes expensive.
For Saskatchewan SMBs, especially in Regina and Saskatoon, the right question isn't whether a national MSP can answer the phone. It's whether they can meet your on-site expectations, support your compliance obligations, and keep identity sprawl under control without making your team carry the load.
Your Next Step and a Local Audit You Can Actually Book
Don't sign a long contract until you've done three things. First, get an IT health check to surface the obvious gaps. Second, ask for a formal infrastructure and identity security audit that turns those gaps into a board-ready report. Third, run a limited proof of concept with the shortlisted provider before you commit to multi-year coverage.
That sequence matters because it separates sales polish from operational competence. If the provider is serious, they'll welcome scrutiny on tenant hardening, access governance, backup testing, and escalation paths. If they push back, you've learned something useful before you've handed them the keys.
Accelerate IT Services Inc. works with Saskatchewan organisations that need managed IT service solutions, identity governance, and practical security reviews tied to day-to-day operations. If you're weighing PIPEDA exposure, Microsoft Entra ID hardening, or a move away from break-fix support, visit Accelerate IT Services Inc. and start with a local conversation about your environment.
Secure Your Corporate Identity & Infrastructure
Managing access risks and maintaining platform compliance is the foundation of operational resilience for Canadian SMBs. Don't wait for a compliance audit or a security event to find hidden vulnerabilities in your cloud tenants.
Take a proactive step to protect your business operations:
- Request a Local Audit: Secure a detailed IT infrastructure and identity security review for your specific environment.
- Get Started Today: Access our Identity Security Assessment Framework.


