
You're probably already seeing the gap. A clinic, accounting firm, or municipal supplier has Microsoft 365 accounts everywhere, a few old joiner-mover-leaver issues nobody got around to cleaning up, and one suspicious sign-in buried in a noisy inbox. That's exactly where identity monitoring services earn their keep, not as a consumer add-on, but as a control plane for business access, privileged activity, and exposed credentials.
Canadian fraud pressure makes that gap expensive. The Canadian Anti-Fraud Centre reported $567 million in fraud losses in 2023 and 108,878 fraud reports that year, then $637 million across 165,484 reports by 2024 in its public reporting cycle, which is a blunt reminder that identity exposure doesn't stay theoretical for long (Canadian fraud-loss context). In Saskatchewan, Calgary, and Toronto, the right question isn't whether identity risk exists, it's whether your team sees it before it becomes a cleanup project.
What Identity Monitoring Actually Catches in a Canadian SMB
A Regina clinic I'd call “typical” had a former employee's Microsoft 365 account left active long after departure, while a senior accountant's credentials also showed up in a dark-web listing. That combination is how small governance misses turn into real exposure. If someone had tried to use the stale account, or if the leaked credentials had been replayed against email or finance systems, the clinic could have been looking at a messy privacy incident instead of a manageable internal cleanup.

The signals worth paying attention to
Identity monitoring services are useful because they watch for the early indicators most perimeter tools miss. That includes suspicious sign-ins from unfamiliar geographies, impossible travel patterns, MFA fatigue behaviour, unexpected OAuth consent grants, and privilege changes that shouldn't be happening on a normal Tuesday.
Practical rule: if the alert only appears after a breach report is filed, the control arrived too late.
Traditional antivirus and firewalls still matter, but they don't see the same thing. They can flag malware, blocked traffic, and endpoint abuse. They usually won't tell you that a dormant account is still active, a privileged user just gained access they shouldn't have, or a compromised credential is being tested against cloud services from somewhere odd.
Why this matters for executives
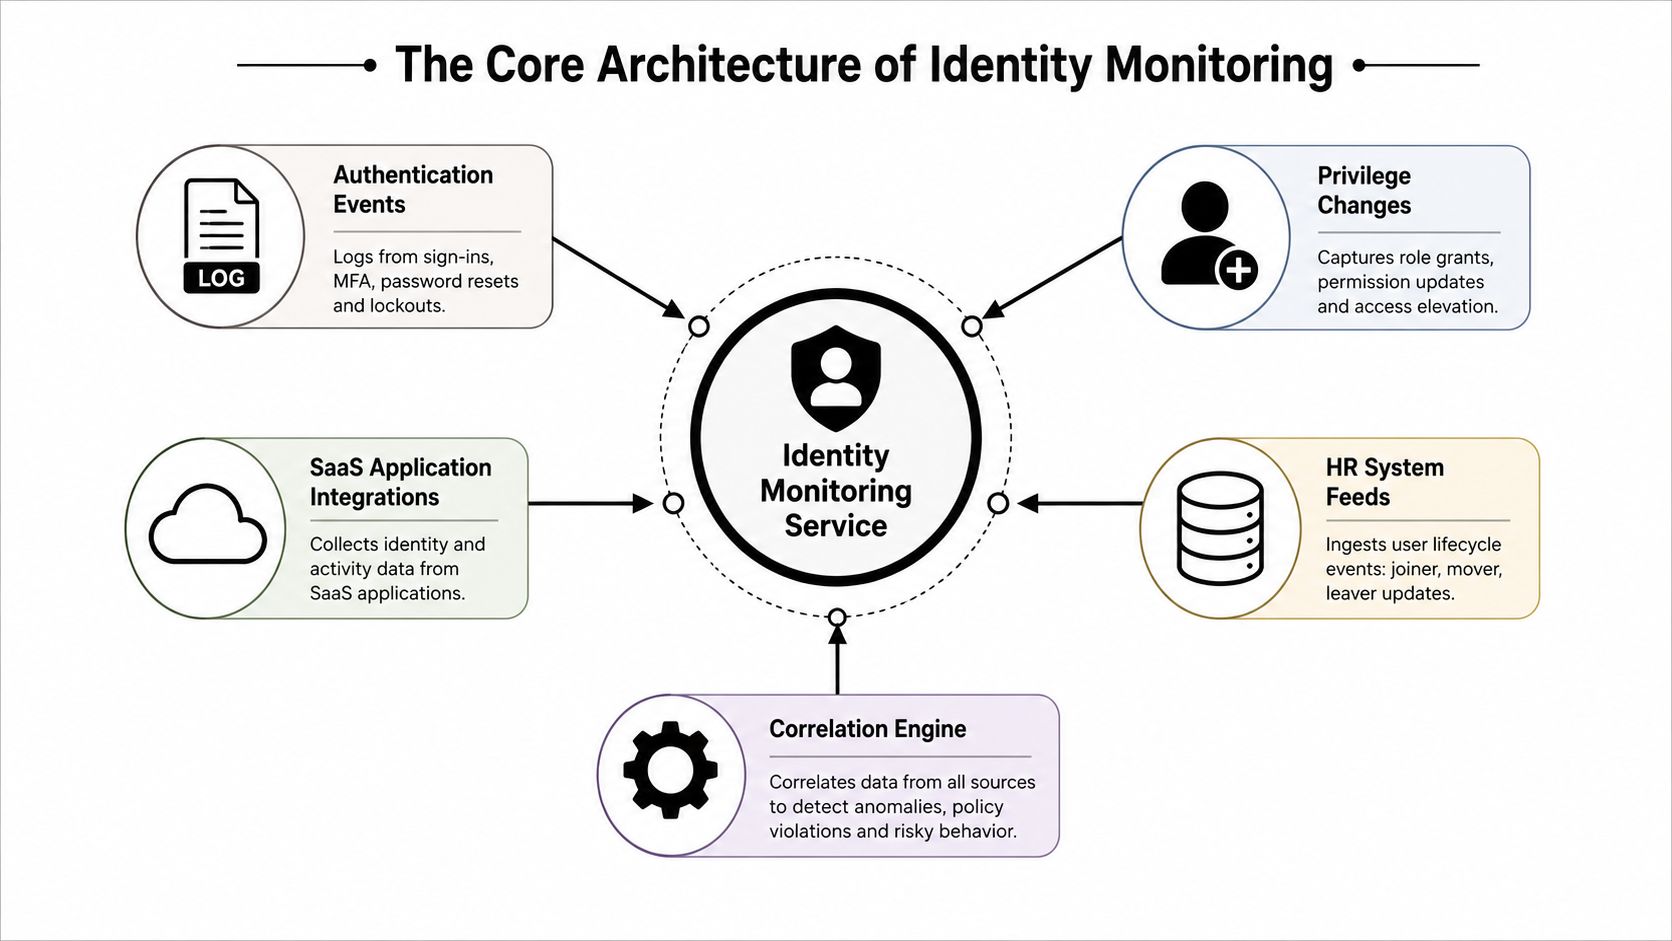
The easiest way to think about identity is as an observable control plane, not a static directory. Palo Alto Networks' guidance on identity visibility and intelligence describes the modern model as a mix of authentication events, privilege changes, and entitlement data that gets correlated across systems, including hybrid environments (identity visibility and intelligence).
That matters because identity issues show up before data loss does. A sign-in anomaly is often the first visible clue that personal data, finance records, or patient information may be at risk. For a Canadian SMB, especially one handling regulated data, that makes monitoring a stronger business control than periodic spreadsheet reviews of access.
The internal perimeter is gone, and the identity layer is now where the attack surface lives. For a broader view of that shift, see why identity security is the new perimeter for Canadian enterprises.
The Core Architecture Behind Modern Identity Monitoring
Identity monitoring only works when it stops pretending identity is a single system. In practice, it has to collect signals from Microsoft Entra ID, on-premises Active Directory, privileged access management vaults, SaaS apps, and governance tools, then line those signals up in a common model so the platform can spot drift, misuse, and anomalies. That's the technical difference between a useful control and another dashboard nobody reads.
How the data actually moves
Identity sources don't behave the same way. Some expose clean APIs, some rate-limit aggressively, and some only become useful when the system listens for push events instead of polling. The monitoring layer has to handle both pull-based API collection and push-based eventing if it wants near-real-time visibility across a hybrid estate.
That's why the better mental model is a security camera network. One camera feed tells you a lot. A central recorder that correlates motion across multiple cameras tells you much more, especially when the suspicious behaviour happens across time, systems, and user roles. The point isn't more noise, it's better correlation.
A monitored identity stack usually needs these layers working together:
- Credential and dark-web monitoring to surface exposed usernames, passwords, and associated identity data.
- MFA and Conditional Access integration so the service understands policy enforcement, not just raw sign-ins.
- PAM session recording for privileged activity that should be traceable later.
- SIEM and SOAR correlation so alerts can join the rest of the security workflow.
- Behaviour-based anomaly detection to catch patterns, not just individual events.
What good architecture changes
When the layers are connected properly, the service can do more than alert. It can show that a risky sign-in, a privilege bump, and an OAuth grant all belong to the same event chain. That's the difference between a ticket and a response.
Don't buy a tool that only watches one source and calls itself comprehensive. In a hybrid Microsoft 365 environment, that's just selective blindness.
If you want the IAM side mapped to the rest of the cloud stack, the most useful companion reading is identity and access management for cloud security. It's the same problem viewed from the control architecture side.
Comparing Consumer, MSP, and Enterprise Identity Monitoring
Most SMBs start with the wrong product category because the marketing sounds reassuring. Household identity protection is built for a person checking a credit file. That is not the same thing as protecting corporate Microsoft 365 access, finance applications, or patient records. If you run a business, the control has to match the business risk.
| Tier | Coverage Scope | Conditional Access Integration | Compliance Reporting | Remediation Workflow | Typical Fit |
|---|---|---|---|---|---|
| Consumer | Mostly credit-focused, personal identity signals, and basic exposure alerts | Minimal or none | Thin, mainly consumer-facing summaries | Usually self-service and reactive | A household, not a business tenant |
| MSP-delivered | Multi-tenant monitoring tied into managed Microsoft 365, endpoint, and helpdesk operations | Practical integration with tenant policies and response workflows | Better for Canadian SMB evidence packs and incident tracking | Managed response, ticketing, and containment steps | Regina, Saskatoon, and Moose Jaw SMBs that need hands-on support |
| Enterprise | Dedicated identity governance, Microsoft Entra ID P2, SIEM/SOAR pipelines, and custom controls | Deep, policy-aware, and built for complex environments | Strongest audit trail and reporting depth | More automation, more orchestration, more internal ownership | Larger regulated environments and multi-site operations |
The right fit is usually obvious
A 12-person accounting firm in Moose Jaw does not need a sprawling enterprise stack. It needs tight Microsoft 365 controls, visible privileged access, and a response path that a small team can run. An MSP-delivered model is usually the sensible choice there because it ties monitoring to action without demanding a full security operations team.
A 120-person healthcare network in Saskatoon is a different problem. That environment is usually better served by enterprise-grade governance, especially if it already runs formal access reviews, role-based administration, and SIEM correlation. The cost of getting it wrong is larger, and the reporting burden is heavier.
Consumer tools still have a place for individual households, but they are the wrong answer for corporate identity risk. If a vendor talks mostly about credit scores and family plans, keep walking. You need visibility into accounts, entitlements, and access policy, not just consumer alerts.
PIPEDA, HIPAA, and the Compliance Triggers That Demand Monitoring
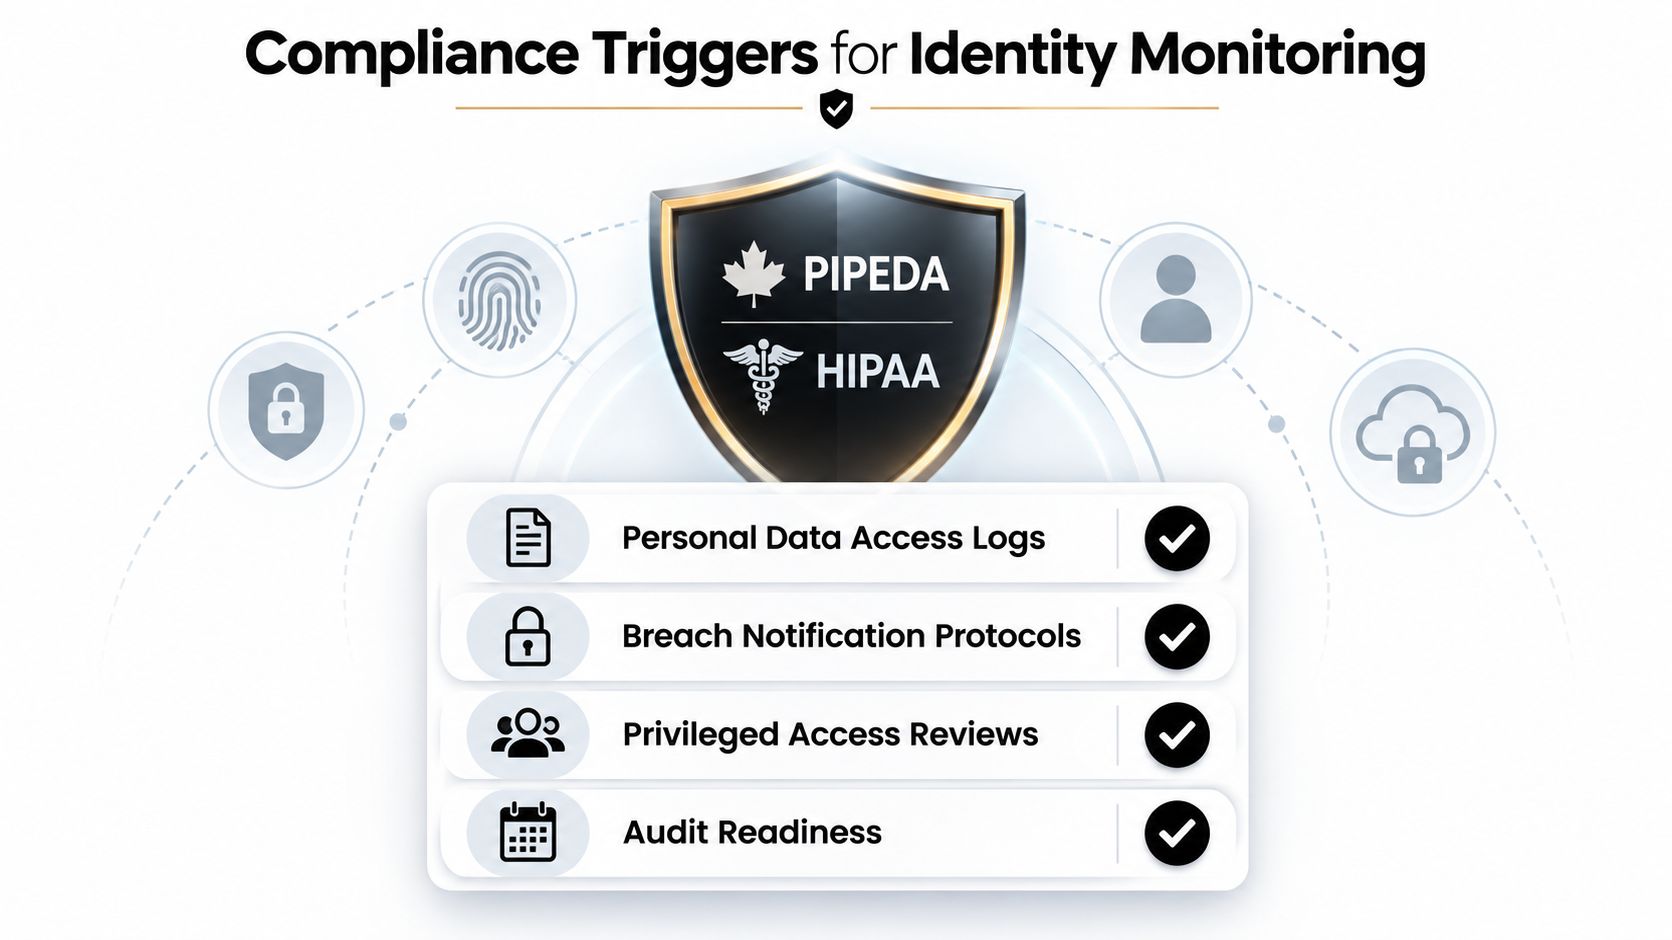
A weak access model turns privacy work into cleanup work. Under PIPEDA, organizations are expected to use reasonable safeguards, and continuous identity visibility is a practical safeguard when the environment holds personal or health information. In a Microsoft 365 tenant or a hybrid setup, that means watching account changes, entitlement drift, and privileged access before they turn into reportable problems.
Healthcare raises the bar in practice. Saskatchewan clinics that handle cross-border referrals or U.S.-linked research data need unique user identification, automatic logoff, and audit controls that stand up to review. If you cannot show who touched what, when, and under which role, your audit trail is too thin to defend.
The operational checkpoints that matter
Identity monitoring becomes a real compliance control only when it supports daily governance work. That means:
- Joiner-mover-leaver synchronization so departures and role changes are reflected quickly.
- Periodic access reviews so stale rights do not linger in Microsoft 365 and related systems.
- Segregation of duties for privileged roles so one person cannot control everything.
- Audit-ready logging that links identity events to remediation actions.
Canadian privacy teams also have to treat identity drift as a practical risk signal, not a theoretical one. If an account lingers after someone leaves, or a role expands without review, the control failure is already in the tenant. The fraud-loss context in Canada makes that problem harder to ignore, because identity events often show up before the rest of the incident does (Canadian fraud-loss context).
For healthcare-focused buyers, the policy discussion should stay tied to testing and evidence. The new 2026 HIPAA compliance rules resource is useful as a reference point beside your own access and audit practices, especially if your clinic handles U.S.-linked data or has to satisfy mixed expectations. It does not replace policy work, but it does keep the compliance conversation grounded in current control expectations.
A proper risk review should also look at identity exposure, not just network defenses. If you want a structured way to assess that gap, use threat risk assessment as part of the same governance conversation.
Building the ROI and Risk Case for Identity Monitoring
Finance leaders do not buy monitoring because it sounds current. They buy it when it cuts cleanup costs, reduces exposure, and gives them a cleaner audit story. In Canadian SMBs, that case is stronger than many vendors admit, because identity failures create direct operational drag, and every missed event adds work for IT, HR, and compliance teams.
Where the return shows up
The first return is a smaller blast radius. If a former employee's account is removed quickly instead of lingering, you shorten the window for misuse. That is basic, and basic failures are what create ugly incidents in real tenants.
The second return is faster detection of credential abuse and account takeover. The U.S. Government Accountability Office notes that identity monitoring services scan public records, proprietary databases, and black-market websites for personal data, which is why they can surface exposure outside normal credit-file checks (GAO identity monitoring scope). For a Canadian clinic or Microsoft 365 tenant, the operational value is the speed of the signal, not the consumer framing around it.
The third return is compliance defensibility. A documented monitoring and remediation process looks far better in an audit than a vague promise that someone usually checks access. That matters in regulated clinics and financial firms, where evidence has to stand on its own.
Practical rule: monitoring is detection. Recovery is separate. A credit freeze or account lock is still a different control, and no subscription replaces that distinction.
Why the spend is easier to defend than it looks
The Consumer Financial Protection Bureau says pricing for identity monitoring services varies widely, from a few dollars per month to more than $15 per month (CFPB identity monitoring guidance). The Wellesley handout also notes that some plans run roughly from US$7 to US$80 per month depending on coverage and restoration, which is a useful reminder that the cheapest plan often buys the thinnest coverage (identity theft protection services handout).
The right ROI argument is simple. Compare the monthly cost of monitoring to the time lost when an account stays open too long, the cleanup time after a credential event, and the paperwork tied to a weak audit trail. In a Microsoft 365 or hybrid environment, those soft costs turn into hard labour fast, especially when an MSP or internal IT team has to chase down access reviews, notifications, and remediation steps after the fact.
For Saskatchewan SMBs, that is the trade-off. You are not buying a feel-good consumer extra. You are buying a control that shortens response time, tightens accountability, and gives privacy and security teams something they can evidence when the tenant is under review.
Implementation Checklist and Vendor Selection Questions
Start with scope, not software. If a provider can't tell you exactly how it will cover users, roles, and privileged accounts, the rest of the conversation is noise. You want a clear inventory of Microsoft Entra ID identities, on-premises AD objects, SaaS accounts, and any PAM vaults before anyone talks about dashboards.
A practical setup checklist
- Map the identity estate. Identify employees, contractors, guests, service accounts, and privileged roles.
- Connect the right sources. Bring in Microsoft Entra ID, on-prem AD, SaaS applications, PAM, and, where useful, HR feeds.
- Set a baseline. Decide what normal looks like before alerts start firing.
- Tune thresholds. Reduce obvious noise so the team trusts the alerts.
- Write the runbook. Define who responds, who approves, and what gets escalated.
- Tie remediation to workflow. Make sure detection feeds actual deprovisioning or access review steps.
Questions to ask every vendor
- What Canadian identity data do you monitor? Ask specifically about exposed emails, names, addresses, and other identifiers that matter in Canada, not only U.S.-centric sources.
- How do you support Lifecycle Workflows? If the platform can't align with joiner-mover-leaver processes, it will miss the point.
- How do you align with Conditional Access? A good answer should mention policy awareness, not just raw alerting.
- What does your PIPEDA and HIPAA reporting output look like? Ask for the evidence format, not a sales demo.
- How do you handle dark-web coverage? Make them explain what they see and how they verify it.
For general market comparison work, some teams also review third-party pricing pages like pricing for AI chatbots just to understand how vendor packaging changes with support and automation. That's not identity security advice, but it's a reminder to read the fine print before you buy a tool on headline features alone.
Watch for vague per-user pricing that never explains restoration scope. That usually means you're comparing an alert feed to a real service, and those are not the same thing.
Saskatchewan SMB Playbook for Identity Monitoring
For Regina, Saskatoon, and Moose Jaw, the right move is usually a 30-60-90 rollout that matches local IT capacity. Don't try to solve everything at once. Start with the identities most likely to hurt you, then tighten controls where they matter most.
First 30 days
Inventory Microsoft 365 identities, privileged accounts, and stale access. Then run a quick exposure check on executives, finance staff, and anyone handling patient or client data. If the team can't answer who still has access after termination, fix that first.
Days 31 to 60
Turn on Conditional Access baselines, align Lifecycle Workflows for joiner-mover-leaver events, and connect the monitoring layer to your SIEM or managed SOC. If you work with an MSP, make sure there's a named response path and not just another notification queue. A free IT health check or local audit is the right time to do that, not after a breach.
Days 61 to 90
Tune the alerts, document the runbook, and make the reporting format usable for PIPEDA and HIPAA-aligned evidence requests. In local settings, the expectation should be practical, fast, and supportable. If your provider can't respond locally in the time your operations require, you don't have a real control.
The best identity program is the one your small team can actually operate on a bad day.
If you're comparing service models, it's also worth checking competitive ManageEngine Identity360 quote to see how packaged identity tools are positioned in the market. Just don't confuse quoting software with designing a workable control.
Secure Your Corporate Identity & Infrastructure
Managing access risks and maintaining platform compliance is the foundation of operational resilience for Canadian SMBs. Don't wait for a compliance audit or a security event to find hidden vulnerabilities in your cloud tenants.
Take a proactive step to protect your business operations:
- Request a Local Audit: Secure a full IT infrastructure and identity security review for your specific environment.
- Get Started Today: Access our Identity Security Assessment Framework.
Accelerate IT Services Inc. helps Saskatchewan organizations tighten Microsoft 365 identity controls, improve Conditional Access, and build practical monitoring that fits real operations. If you want a local team that understands regulated clinics, SMB risk, and the difference between alerts and remediation, visit Accelerate IT Services Inc. and book a conversation.


