
Your internal IT administrator starts Monday with a queue of password resets, access requests, endpoint alerts, and software issues. By Friday, the helpdesk work is complete enough to keep the business moving, but the tenant hardening, lifecycle management, infrastructure upgrades, and security reviews remain untouched. On paper, staffing may look adequate. Operationally, the business is running on deferred risk.
A co-managed IT resource calculator should measure more than users per technician. Canadian SMBs in Regina, Saskatoon, Calgary, and Toronto need a model that accounts for endpoints, ticket demand, project delays, after-hours coverage, specialist expertise, and compliance workload. That produces a staffing recommendation executives can use for budgeting, service-level decisions, and risk reduction.
Why Traditional IT Staffing Calculations Fall Short
A headcount-only calculation assumes every employee creates roughly the same support demand and every technician spends most of the day on predictable work. Neither assumption holds for a growing Canadian business. A user with several business applications, privileged access, remote-work requirements, or regulated data creates a different workload from a user with a single standard workstation.
The most common failure is confusing nominal capacity with usable capacity. An internal administrator may be responsible for helpdesk tickets, Microsoft 365 administration, vendor coordination, endpoint maintenance, backup checks, security alerts, onboarding, offboarding, and infrastructure projects. When urgent requests arrive continuously, strategic work gets postponed first. The business then interprets the delay as a project-management issue rather than a capacity problem.
A small internal team can know the environment extremely well and still lack the coverage needed to operate it safely. A co-managed model adds external capacity without removing internal ownership, which is the practical distinction between internal IT and an MSP partnership.
Hidden operational drains
Traditional calculators usually miss four workload sources:
- Reactive firefighting: Repeated incidents consume time that would otherwise go to patching, hardening, documentation, and architecture.
- Project backlog: Deferred migrations and upgrades create technical debt. The longer they wait, the more coordination and remediation they require.
- Peak demand: Averages hide login surges, new-starter waves, major application rollouts, and incident clusters.
- Security and compliance: Access reviews, log monitoring, vulnerability remediation, evidence collection, and breach processes require deliberate engineering time.
This matters in Saskatchewan because the local technology labour market is expanding quickly. Saskatchewan's tech sector reached 5,489 employees in 2023, after adding 2,858 workers between 2019 and 2023, with the province reporting 108.6% growth since 2019 and 161.6% growth since 2016. The sector represents 1.1% of Saskatchewan's total workforce, according to the State of Saskatchewan's Technology Sector report. For SMBs in Regina and Saskatoon, that growth reinforces the need to plan capacity instead of assuming an internal generalist can absorb every new requirement.
Practical rule: If your internal IT team has no protected time for security hardening or infrastructure lifecycle work, your current staffing level is already too low, regardless of the user-to-technician ratio.
The Four Critical Data Points for Accurate Sizing
Start with operational evidence, not a preferred staffing outcome. Gather the four inputs below from ticketing, endpoint management, identity, and project records, then validate them with the people doing the work.
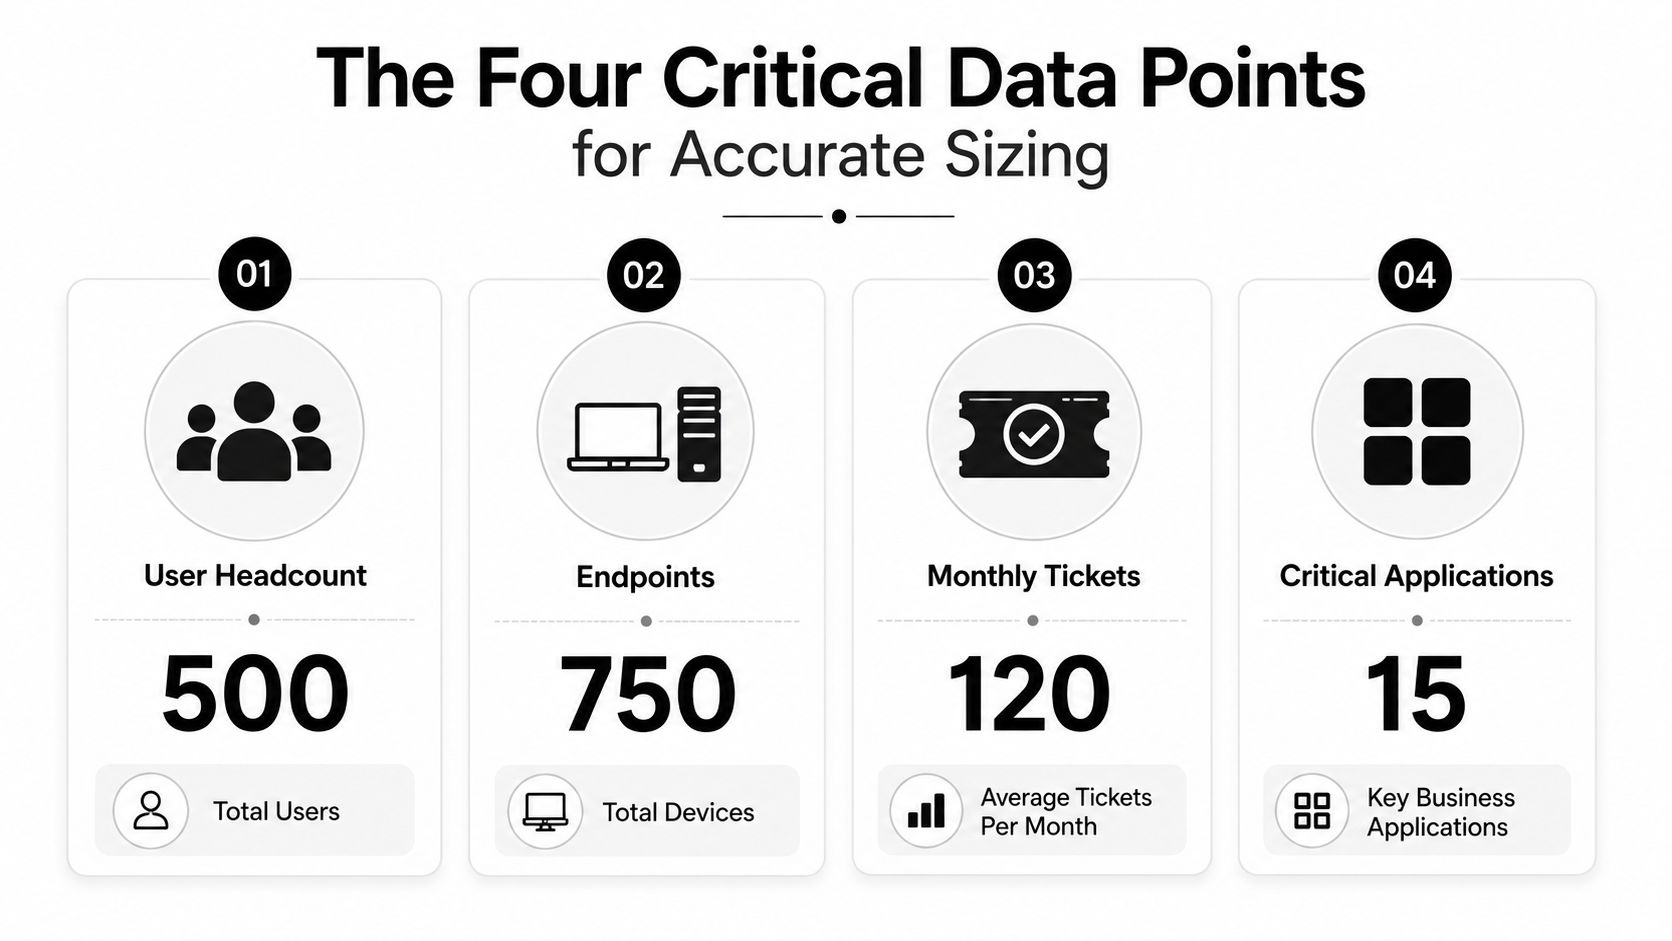
User headcount
Count active users who require support, not just permanent employees. Include contractors, seasonal staff, remote workers, and service accounts only where they create human administration or access-review work. User count establishes the baseline for identity support, onboarding, offboarding, licensing, and helpdesk demand.
A growing employer base makes this especially relevant in Canada. 98% of Canadian employer businesses are small businesses, according to the Canadian managed services industry summary. SMB leaders should therefore treat resource planning as an operating discipline, not an enterprise-only exercise.
Endpoints
Count workstations, laptops, servers, and other managed devices. A user-to-device ratio can vary widely, especially where employees use multiple devices, production systems, shared terminals, or local servers. Endpoint count affects patching, monitoring, encryption, replacement planning, backup, and incident response.
Pull the number from your device-management platform rather than from procurement records. A stale asset list produces a false sense of control.
Average monthly ticket volume
Use a representative period and separate incidents from requests. Password resets, access changes, software problems, device failures, and recurring application issues consume different amounts of technician time. Record reopened tickets and escalations, because a low closure count doesn't necessarily mean low demand.
As an operational example, a 120-user organization with roughly 140 total endpoints averaged 180 tickets per month. Its lone internal IT administrator was consumed by basic helpdesk work, leaving no time for infrastructure lifecycle management or security hardening. That pattern illustrates why ticket volume must sit beside headcount in the calculator.
Deferred projects
List active projects that have been delayed because daily support takes priority. Include tenant hardening, secure infrastructure migrations, backup testing, application replacement, network changes, identity governance, and endpoint refreshes.
A useful measure is not just the number of projects, but the hours the internal team spends reacting instead of progressing them. Monitoring tools such as network monitoring software can help expose recurring infrastructure work that ticket summaries often hide.
Calculating Co-Managed IT Resources Step by Step
A reliable estimate begins with staffing depth, assigns service coverage, and then tests whether the proposed model meets operational requirements. Canadian co-managed programs are commonly positioned for firms with roughly 30 to 300 users and 1 to 5 internal IT staff, according to Canadian co-managed IT service guidance. That range is a useful screening point, not a substitute for workload analysis.
Step one, establish the baseline
Use the user count to estimate frontline support capacity. A cited benchmark describes a 4:1 technician-to-client ratio, compared with an industry norm near 12:1, alongside 93% first-contact resolution and a 1-hour critical response SLA. Those figures are useful only when the provider defines what the ratio, resolution rate, and response commitment include.
Then adjust for endpoints and tickets. A firm with fewer users but many devices, servers, or business applications may require more operational capacity than headcount suggests.
Step two, apply the Project Friction Factor
The Project Friction Factor converts hidden operational drag into a visible planning variable. Score the internal team based on how much capacity is consumed by:
- recurring incidents and rework,
- peak ticket periods,
- technical debt,
- deferred infrastructure projects,
- security hardening,
- vendor coordination,
- documentation and change control.
A high score means the calculator should recommend more external capacity or a narrower internal scope. The purpose isn't to create false precision. It forces executives to acknowledge that a technician who spends the day firefighting cannot also deliver strategic projects.
Step three, add coverage and specialist requirements
Decide which responsibilities the MSP will own. The practical buckets are daily break/fix, after-hours coverage, security operations, and project work. Add specialist depth for Microsoft Entra ID security reviews, Conditional Access, tenant hardening, backup and recovery, secure migrations, and Tier 3 escalation.
Regulated firms need a separate compliance adjustment. The provided Canadian pricing guidance says compliance-heavy environments can add 15 to 20 hours of engineering and documentation work per month, covering access reviews, log monitoring, multifactor authentication reporting, and vulnerability remediation. Apply that workload when modelling finance, legal, and healthcare operations, rather than burying it inside a generic support tier.
Step four, validate cost and service levels
Canadian SMB co-managed pricing is commonly modelled at CA$130 to CA$180 per user per month on top of internal IT salary. For a 75-user firm, that implies approximately CA$9,750 to CA$13,500 per month for the MSP layer alone, based on the Canadian co-managed MSSP pricing model.
| User Count | Monthly Cost Range (CA$) | Annual Cost Range (CA$) |
|---|---|---|
| 50 | Approximately CA$13,583 to CA$18,167 | CA$163K to CA$218K |
| 100 | Approximately CA$23,000 to CA$32,167 | CA$276K to CA$386K |
| 200 | Approximately CA$44,333 to CA$61,833 | CA$532K to CA$742K |
These projections should be tested against response times, escalation ownership, after-hours monitoring, security scope, and overflow handling. For identity-focused planning, guidance on how to avoid policy failures with Ollo provides useful context for evaluating Conditional Access and zero-trust controls alongside staffing.
Real-World Scenarios and Calculator Recommendations
A calculator should produce different recommendations for businesses with similar headcounts when their operational conditions differ. The following anonymized scenarios show why.
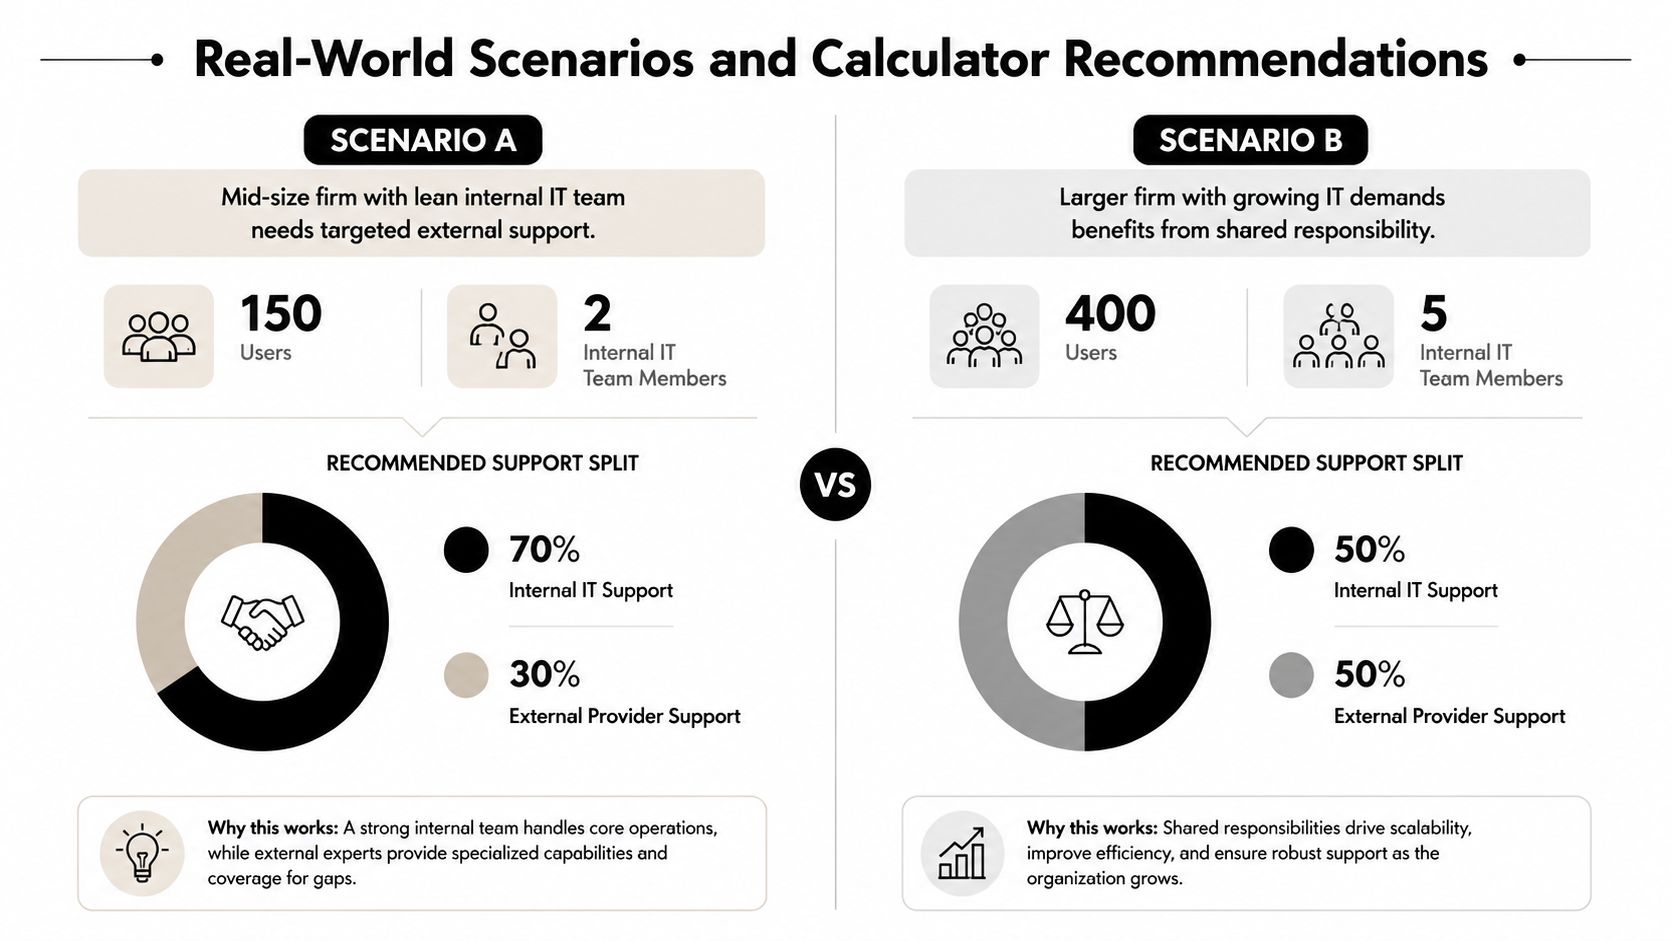
Scenario A, the overloaded internal manager
A 150-user firm had an internal IT manager and a significant amount of daily operational pressure. The calculator used user count, ticket demand, project backlog, and the need to preserve management capacity for strategic work. Based on a target of roughly one Tier 1 or Tier 2 technician per 70 to 80 end-users, it recommended 1.5 to 2 dedicated remote co-managed technicians.
The deployment used a dedicated primary remote resource backed by a broader service desk. That arrangement cleared the helpdesk queue and allowed the internal IT manager to focus on strategic alignment and internal projects. The lesson is direct: the right recommendation isn't always a whole new internal hire. It may be external frontline capacity with escalation depth behind it.
Scenario B, the regulated healthcare operation
A healthcare organization may have a different staffing requirement even when its support queue appears manageable. Its calculator inputs must include identity governance, access review evidence, log monitoring, multifactor authentication reporting, endpoint protection, backup validation, and vulnerability remediation.
PIPEDA requires organizations to report breaches involving personal information when there is a real risk of significant harm, notify affected individuals and the Privacy Commissioner of Canada, retain breach records for two years, and keep records of all breaches regardless of the harm threshold, as described by the Office of the Privacy Commissioner of Canada. That obligation affects staffing design because someone must maintain the controls and produce reliable evidence.
Microsoft Entra ID Governance adds practical lifecycle work. Administrators create Lifecycle Workflows in the Entra admin centre, and Microsoft designed the feature to manage users across the three lifecycle phases of their relationship with an organization. Workflow events remain available in Audit Logs for later review, as documented in the Microsoft Entra Lifecycle Workflows documentation and the related workflow audit guidance.
A compliance-adjusted calculator should therefore add engineering and documentation capacity, not merely attach a security product to the same support estimate.
Canadian cybersecurity conditions reinforce the need for this adjustment. One 2026 Canadian report cited 26% of Canadian businesses as having written cybersecurity policies, while another reported average attacks on large enterprises rising from 191 to 342, according to Cybersecurity Canada's 2026 report. These figures don't determine technician count by themselves, but they do show why security work belongs inside the resource model.
Evaluating ROI and Service Level Tradeoffs
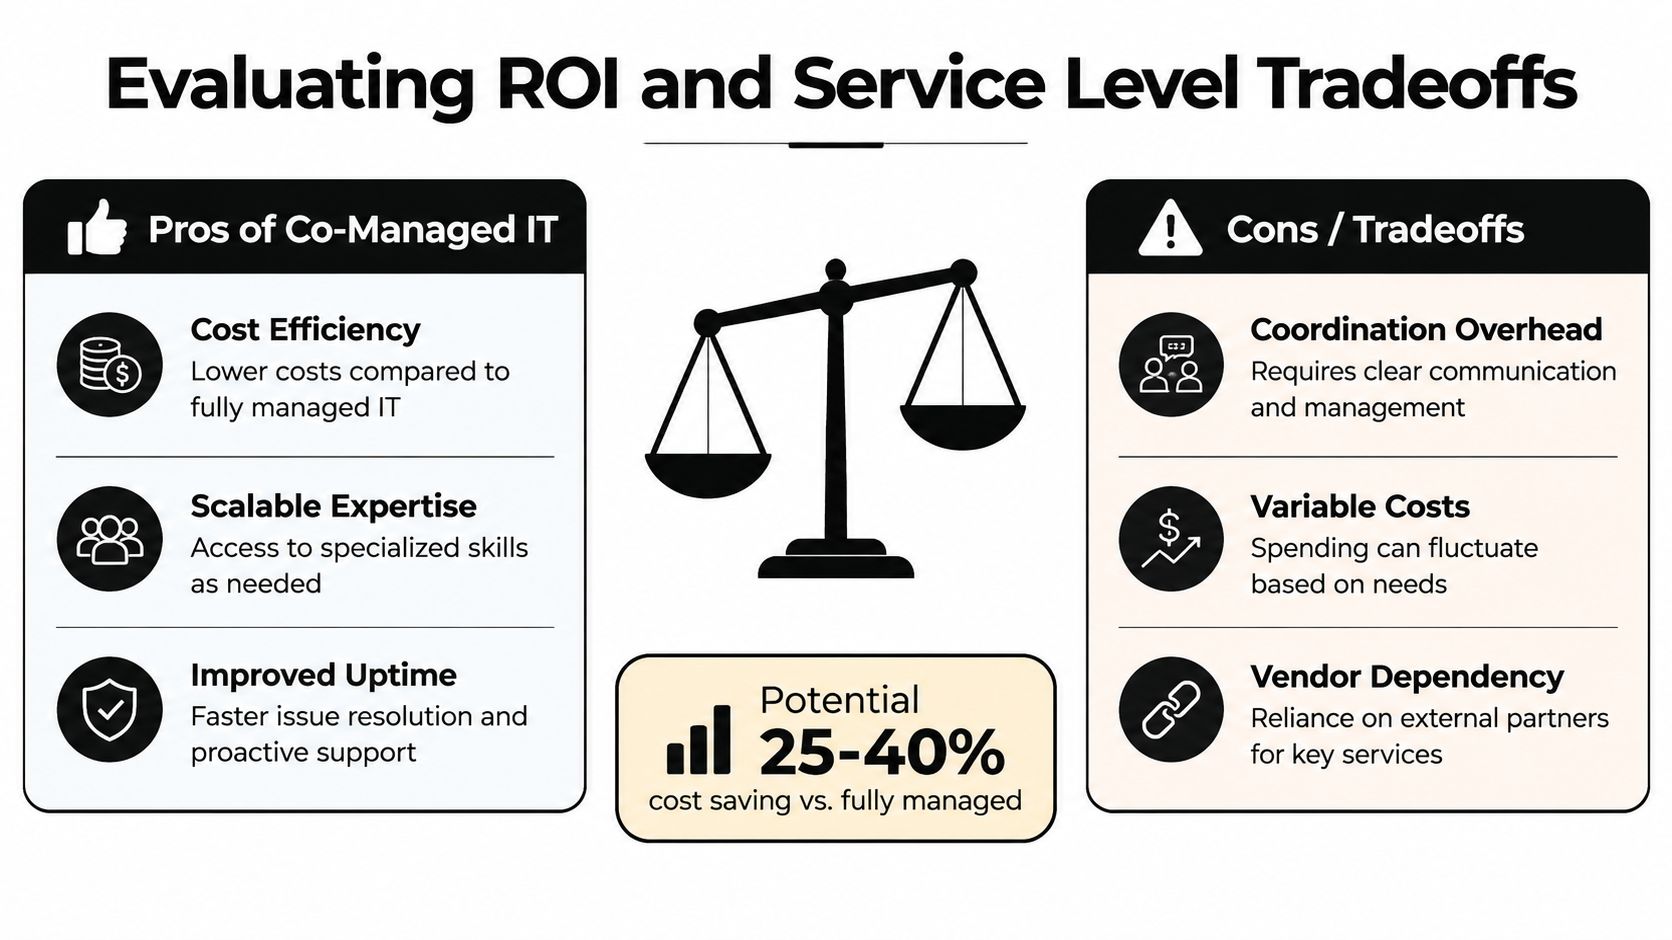
Co-managed IT delivers value when it removes a specific bottleneck. The business keeps internal knowledge and decision-making while obtaining external coverage for work that its own team can't perform consistently. That may include helpdesk overflow, after-hours monitoring, security operations, Tier 3 escalation, patch-management backup, or a secure cloud migration.
Where the return comes from
The strongest return usually appears in capacity released, not in a simplistic comparison between invoices. If an internal manager stops spending every day on basic tickets, the business can move security projects, lifecycle work, and infrastructure improvements forward. That can reduce operational exposure while improving retention for staff who want to perform higher-value technical work.
A fully managed model may make more sense when the company doesn't intend to maintain internal IT ownership. Co-managed IT is the better fit when internal staff understand the business and should remain accountable, but lack coverage or specialist depth.
Service levels determine the economics
A low monthly price with vague responsibilities isn't a saving. Define:
- Response ownership: State who receives tickets first and when internal staff are involved.
- Critical incidents: Specify the response target, escalation path, communications cadence, and decision authority.
- Security scope: Identify whether monitoring, remediation, identity governance, endpoint protection, backup testing, and incident support are included.
- After-hours coverage: Clarify whether the provider monitors, responds, or only escalates.
- Reporting: Require useful evidence for tickets, changes, access reviews, vulnerabilities, and recurring incidents.
Coordination overhead is real. Internal teams must share documentation, approve changes, and maintain clear ownership boundaries. Vendor dependency is also a risk if the provider controls knowledge or tools without documented exit procedures.
Executive test: Approve co-managed IT when it gives your internal team protected capacity, measurable coverage, and security depth. Reject it when it merely adds another inbox.
Security-inclusive managed services can reach approximately CA$230 per user per month and may bundle CIS-aligned controls, according to Canadian managed IT pricing guidance. That makes scope discipline essential. Compare like with like, especially for firms in regulated sectors and for organizations migrating infrastructure into Microsoft 365 or Azure.
Secure Your Corporate Identity and Infrastructure
A resource calculation is useful only if it leads to safer execution. If the model reveals that your internal team has no time for access reviews, tenant hardening, endpoint remediation, or backup validation, treat that result as a risk finding. Staffing capacity and identity security are connected because uncompleted control work leaves accounts, devices, and data exposed.
Microsoft Entra ID Governance can organise joiner, mover, and leaver processes, while Audit Logs provide a record that administrators can review later. For a broader programme, identity and access management for cloud security should sit alongside Conditional Access reviews, privileged-access controls, endpoint protection, recovery planning, and documented incident procedures.
Canadian SMB executives should also distinguish a co-managed technician requirement from a permanent leadership vacancy. If the organisation needs to recruit or assess senior cloud capability, a specialist resource on cloud infrastructure staffing can help define the role before the business commits to an internal hire. The right answer may be a technician, a security specialist, a project resource, or a combination of these.
Do not wait for an audit or security event to reveal hidden weaknesses in your cloud tenant. Use the calculator to identify workload, then commission a local review that tests whether your controls, ownership model, and service levels match the risk.
Secure Your Corporate Identity & Infrastructure
Managing access risks and maintaining platform compliance is the foundation of operational resilience for Canadian SMBs. Don't wait for a compliance audit or a security event to find hidden vulnerabilities in your cloud tenants.
Take a proactive step to protect your business operations:
- Request a Local Audit: Secure an IT infrastructure and identity security review designed for your specific environment.
- Get Started Today: Access our Identity Security Assessment Framework.
Accelerate IT Services Inc. helps Canadian SMBs assess co-managed IT capacity, strengthen Microsoft Entra ID and cloud controls, and cover daily support, security operations, and infrastructure projects. Visit Accelerate IT Services Inc. to request an environment-specific review and turn your staffing estimate into an actionable security and operations plan.


