

Most advice on Best Managed IT Service Providers Canada 2026 starts in the wrong place. It starts with the biggest brand, the longest national footprint, or the slickest marketing page, then pretends those things matter more than whether the provider can support your users in Regina, Saskatoon, Calgary, or Toronto when something breaks at 8:15 on a weekday morning.
That's the wrong lens for Canadian SMBs. The filters are sharper, and they're operational, local technician availability, response-time guarantees, identity-first security, and pricing that doesn't punish you for emergencies. In a market this crowded, the provider that looks strongest on a ranking page can still be the wrong fit for your risk profile.
Why the Biggest MSP Is Rarely the Best Fit for Canadian SMBs
The biggest MSP usually wins on brand reach, not on day-to-day fit. For a Prairie business, that distinction matters because service quality shows up in response discipline, escalation clarity, and whether the provider can solve problems without turning every incident into a billing event.
The Canadian market has also become too fragmented to trust size alone. Independent directories now list hundreds of providers across Canadian cities, which means buyers aren't choosing from a neat national shortlist, they're sorting through a crowded field where verification, scope, and regional coverage matter more than logo recognition.
What actually breaks first in bad MSP relationships
A weak fit usually fails in the same places, delayed response, fuzzy scope, and support teams that don't understand your environment. If a provider can't explain how it handles after-hours incidents, tenant security, or onsite escalation in your city, it's not ready for a business that depends on uptime.
Practical rule: If the MSP can't tell you who handles a critical ticket in your province, what happens after hours, and how fast onsite support can be dispatched, keep looking.
That's why geography matters so much in 2026. Many national roundups still lean heavily toward Toronto-based firms, while Prairie buyers are left evaluating a much thinner field of local or regional options that can show up in person when the situation demands it.
A local or regional provider isn't automatically better. But for SMBs outside the Toronto core, the best option is often the one that combines local response with national-grade security and cloud operations, not the one with the loudest market presence.
The Canadian Managed IT Market in 2026
Canada's managed services market is big enough now that MSP selection is a real strategic decision, not a procurement afterthought. Grand View Research estimated the Canadian managed services market at USD 8.61 billion in 2024, with an expected USD 18.33 billion by 2030 and a 13.4% CAGR from 2025 to 2030, which points to a market that keeps rewarding providers with repeatable security, cloud, and support capabilities. For context on how that industry is framed in Canada, see the managed service provider industry overview.
That growth hasn't made buying simpler. It has made the field more crowded, and the best-of lists are still concentrated in a few hubs, especially Ontario and Alberta, while Saskatchewan remains represented by fewer visible anchors such as WBM Technologies (Saskatoon) in national ranking pages. That tells you something important, the market may be expanding, but the vendor selection outside major cities is still thinner.
What the directory data says
The city-level vendor scene is fragmented enough that buyers need a disciplined shortlist process.
| Metric | Value | Implication for SMB Buyers |
|---|---|---|
| Canadian managed services market, 2024 | USD 8.61 billion | MSPs are operating in a mature, competitive category, not a niche service. |
| Projected Canadian managed services market, 2030 | USD 18.33 billion | Buyers should expect more specialization, not less. |
| Projected CAGR, 2025 to 2030 | 13.4% | Providers with standardized operations and security depth are being rewarded. |
| Directory coverage across Canada metros | 165 vetted providers across 8 metros | Local choice exists, but it's uneven by city. |
| Toronto directory coverage | 26 verified providers | Toronto buyers have deep choice, so differentiation matters more. |
| Multi-city Canada comparison coverage | 338+ providers across 99 cities | The market is large enough that verification is mandatory. |
| Canada-wide verified listings | 333+ providers across 20 cities | Regional fit and service scope are crucial buying filters. |
The takeaway is simple. Canadian SMBs are buying in a market that's growing, but also splintering by city, service depth, and compliance posture. If you're in Regina or Saskatoon, you're not looking for the biggest MSP in the country, you're looking for the one that can match your operating reality without creating hidden support gaps.
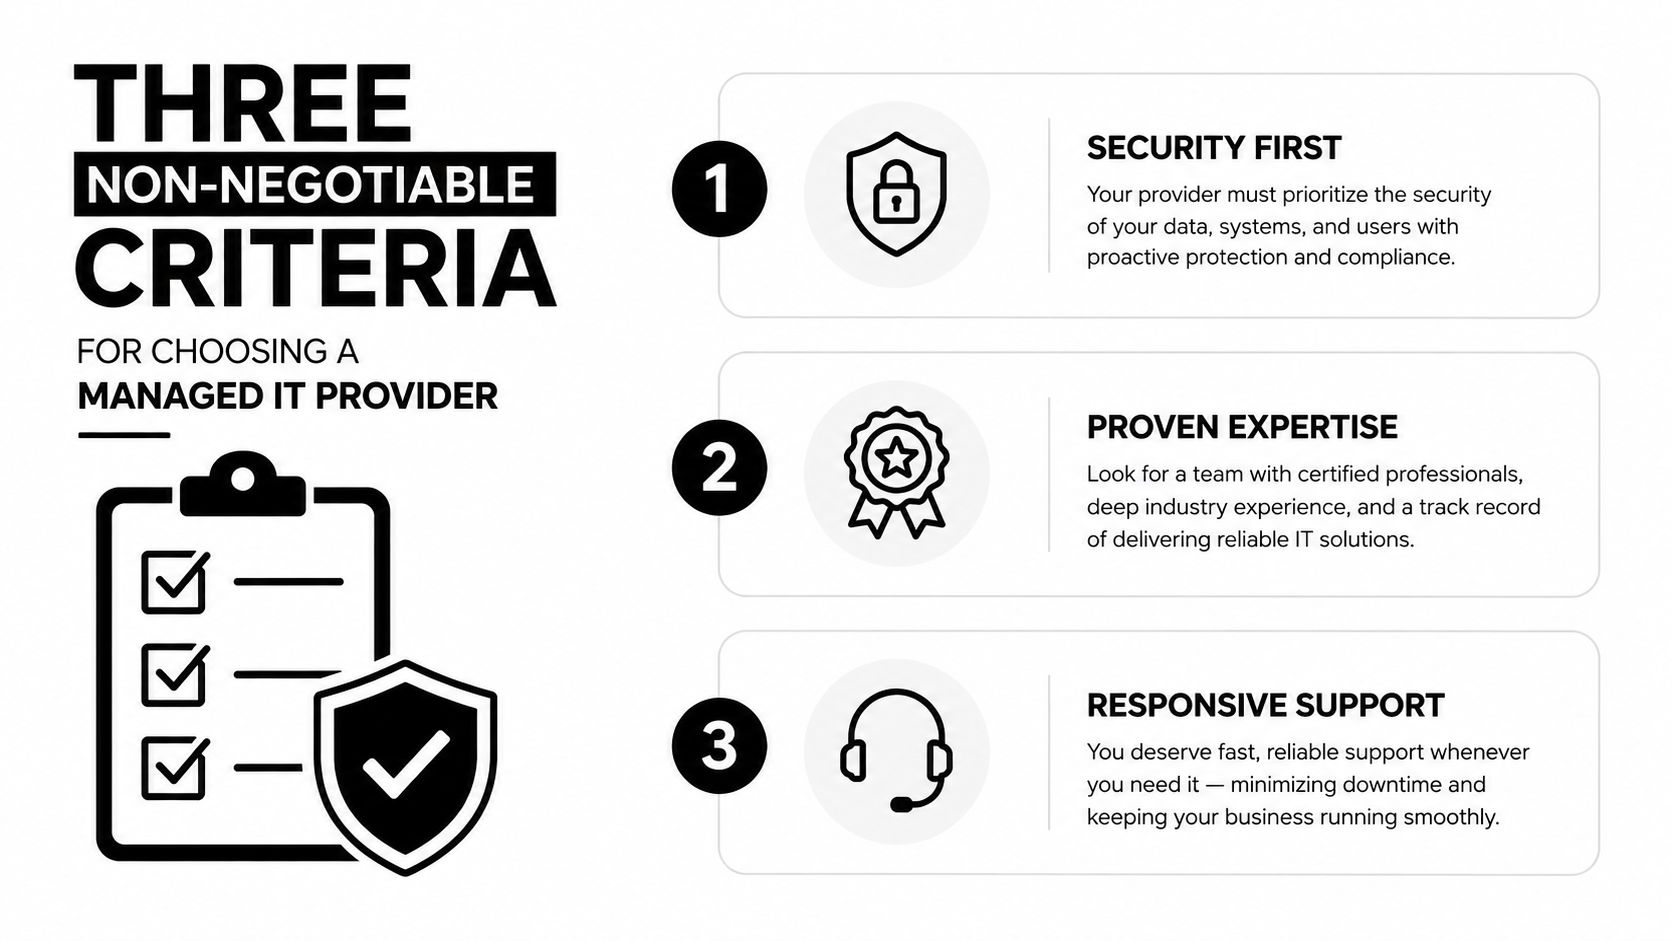
Three Non-Negotiable Criteria for Choosing a Managed IT Provider
The easiest MSP to sell is not the safest one to hire. In 2026, you should be grading providers against three essentials: identity-first security, pricing transparency, and Canadian compliance competence. Anything less leaves too much room for operational surprises.
1. Zero Trust identity and security alignment
Basic antivirus and MFA aren't enough anymore. You want an MSP that can speak clearly about Microsoft Entra ID governance, Privileged Identity Management, phishing-resistant access control, Conditional Access hardening, and how it handles identity verification for remote endpoints.
Ask blunt questions. Does the provider review tenant permissions regularly? Can it explain how it hardens privileged access? Does it know how to reduce the chance that one compromised account becomes a tenant-wide incident? If the answers stay vague, the provider's security model is too shallow for a regulated SMB.
2. Predictable flat-rate pricing with clear SLAs
Billable-hour support punishes you when you need help most. A good MSP gives you fixed monthly pricing and documented service commitments, so a hardware failure, urgent patching job, or after-hours issue doesn't become an unplanned expense.
Hard standard: If critical tickets don't have a clearly stated response commitment, you're buying ambiguity, not support.
That's where SLA transparency becomes a technical issue, not a sales detail. Compare documented response times, uptime promises, escalation paths, and what's included versus what gets billed separately. If emergency work, hardware handling, or off-hours support sits outside the base model, the “cheap” provider often ends up being the expensive one.
3. Canadian sovereignty and compliance expertise
Canadian SMBs in healthcare, financial services, legal, and professional services need a provider that understands PIPEDA, provincial privacy rules, and Canadian data residency expectations. That means more than saying the right things in a pitch deck.
Use how to choose the right IT managed services partner as a practical benchmark when you compare vendors. Ask where data lives, how backups are handled, what audit evidence is available, and whether the provider can support sovereign cloud configurations without improvising under pressure.
If a provider treats compliance as paperwork, it's not ready for regulated workloads.
Core Service Offerings Every Canadian SMB Should Expect
A credible MSP in 2026 has to cover more than break-fix tickets. The baseline is a service stack that keeps users productive, protects identities, and stops routine maintenance from turning into downtime. For Canadian SMBs outside Toronto, that also means the provider can support your region without treating you like a remote afterthought.
The weak providers still lead with generic helpdesk language. The stronger ones show operational depth through 24/7 monitoring, endpoint management, cloud administration, backup discipline, and identity governance built into the same operating model.
The service stack that actually matters
| Service Category | Commodity MSP | Security-First MSP |
|---|---|---|
| Helpdesk and NOC | Business-hours support with slow escalation | 24/7 helpdesk, proactive NOC, and documented escalation paths |
| Endpoint protection | Basic antivirus and ad hoc patching | Managed endpoint controls, patch cycles, and telemetry-driven response |
| Backup and recovery | Backup exists, restore testing is inconsistent | Backup with restore validation and disaster recovery planning |
| Microsoft 365 administration | User setup and password resets | Tenant hardening, permissions review, and secure collaboration management |
| Identity and access management | MFA enabled, little else | Conditional Access hardening, Lifecycle Workflows, Privileged Identity Management, and identity governance |
| Remote access | Legacy VPN default | Zero Trust Network Access and governed access to apps and resources |
If a provider cannot explain how it manages Microsoft 365 beyond password resets and mailbox support, it is reacting to issues rather than managing the environment proactively. Identity deserves the same scrutiny. Identity is the security boundary now, and providers that still build around perimeter thinking are behind the curve.
A few operational signals separate serious providers from commoditized ones. Consistent telemetry, incident traceability, secure onboarding for new users, and cloud migrations that preserve access policies all matter. Microsoft Entra Suite, with Identity Governance, Global Secure Access, and Private Access, fits that model because it replaces legacy VPN habits with controlled access to apps and resources.
Buyers comparing options will see the difference quickly. Commodity MSPs talk about tickets. Security-first MSPs talk about identity, control points, regional response capability, and how they stop a minor issue from turning into a tenant-wide breach. That distinction matters even more for Prairie and Western Canadian SMBs that need serviceability, response clarity, and security controls that do not depend on a downtown Toronto team improvising from a distance.
How Fixed Pricing and Rapid Response Prevent Costly Downtime
Canadian SMBs make a costly mistake when they buy support from a provider that profits from emergencies. Hourly billing for urgent repairs turns every serious incident into a bigger invoice before it turns into a technical fix.
A regional client once dealt with an unexpected firewall hardware failure during peak operating hours. Under a time-and-materials model, emergency provisioning, priority dispatch, and after-hours labour would have created unplanned cost and avoidable delay. With a 15-minute SLA guarantee and fixed monthly pricing, the team validated the failure remotely, deployed a pre-configured standby security appliance onsite, and completed failover without emergency engineering fees or a full business day of downtime.

The service stack that matters
The pricing model matters because the contract shapes behaviour. A low headline rate means little if urgent labour, after-hours work, or replacement hardware sit outside the agreement. In that setup, the bill spikes exactly when the business can least absorb it.
Use fixed monthly pricing with no surprises as the baseline in every serious vendor conversation. It gives you predictable budgeting, faster incident decisions, and fewer excuses when someone needs to act immediately. That is what separates a provider that can support operations from one that only looks inexpensive on paper.
This is not a sales detail, it is an operating control. A good MSP should state, in plain language, what is included, what is excluded, and how it handles critical tickets without turning the incident into a billing negotiation.
Compliance and Data Sovereignty for Regulated Canadian SMBs
Compliance isn't a box to tick after deployment, it's part of the service design. If you operate in healthcare, finance, legal, or professional services, your MSP has to be able to work inside the rules that govern your data, your users, and your audit trail.
A security-led modular stack is usually the right fit. That means identity hardening, endpoint management, backup, and 24/7 monitoring running under one operating model, rather than being stitched together by separate vendors with separate failure points.
What to verify before you trust a provider with regulated data
Start with the basics. Ask where client data is stored, how access is controlled, whether audit-ready documentation is available, and whether the provider can support Canadian data residency without relying on vague assurances.
For teams dealing with payment environments, PCI compliance for WordPress is a useful external reference point because it shows how specific controls and documentation expectations can be in practice. That kind of operational rigor matters more than broad claims about being “compliance-ready.”
You should also ask how the provider verifies remote endpoints, manages privileged access, and supports sovereign cloud configurations. If it can't explain those things in plain language, it may understand the compliance vocabulary but not the operational work.
Regulated buyers should ask for evidence, not slogans. Documentation, access logs, and recovery procedures matter more than a polished capability sheet.
AITS's own positioning fits this style of requirement well because it ties Canadian privacy requirements to real delivery areas like Microsoft 365, cloud enablement, endpoint protection, and backup. That's the right shape for a provider serving privacy-sensitive workloads, especially when the buyer needs both local support and audit-ready operational discipline.
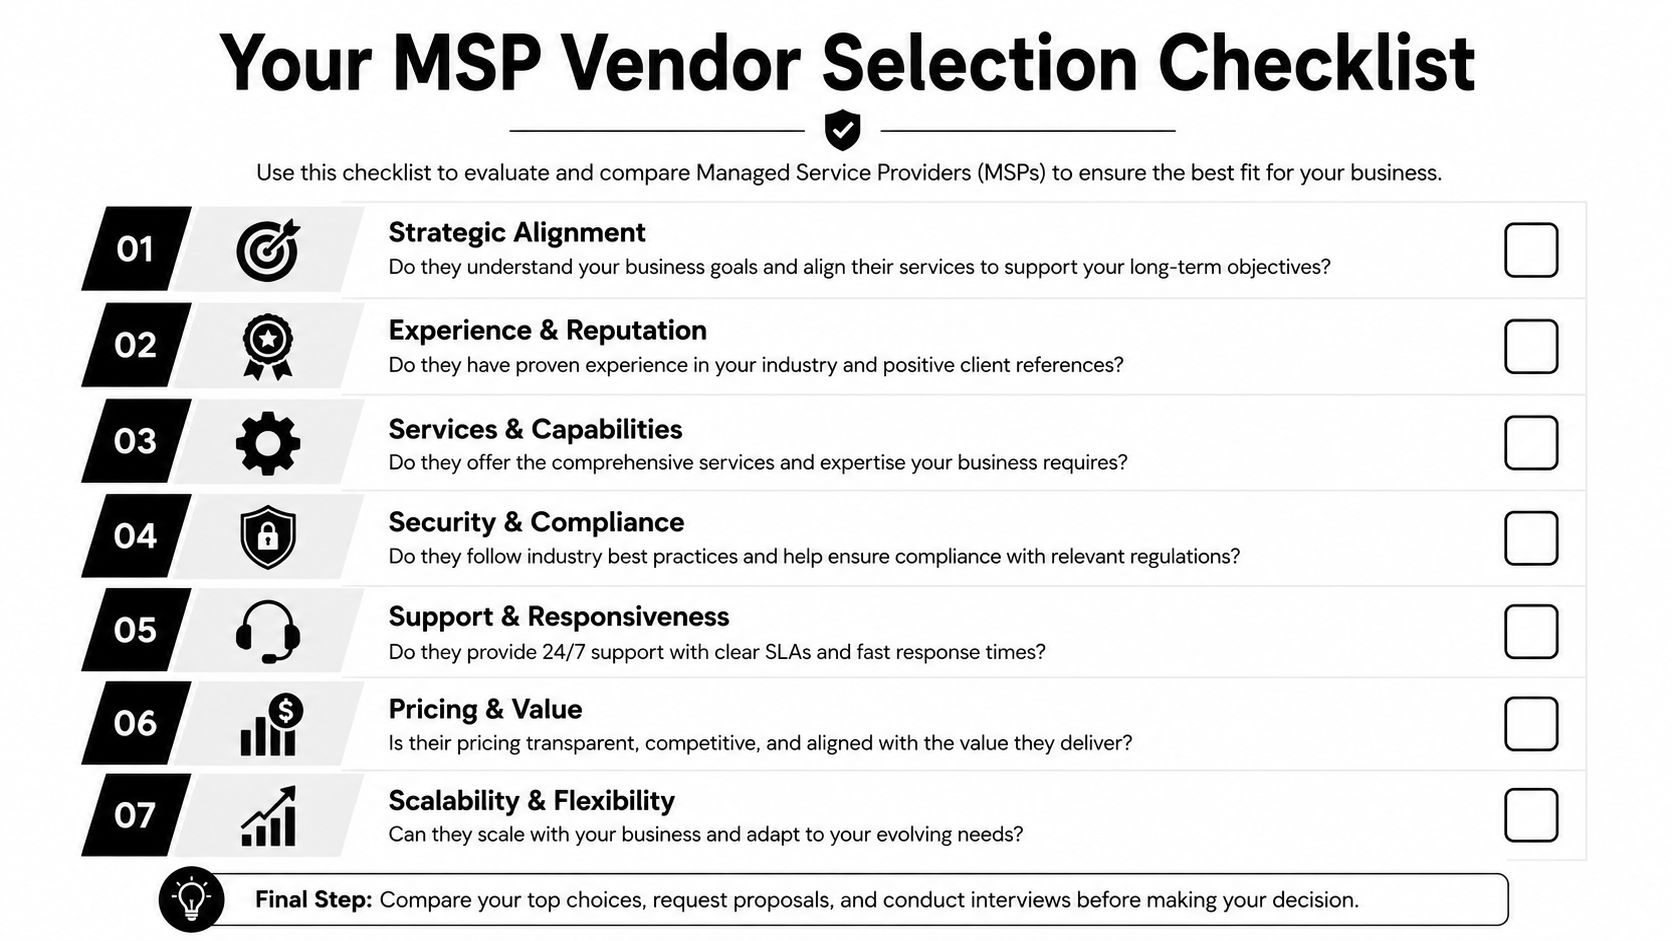
Your MSP Vendor Selection Checklist
Shortlist providers the same way you'd review a major systems change, with evidence, not optimism. The best MSP for a Regina clinic, a Saskatoon manufacturer, a Calgary firm, or a Toronto professional services office isn't just the one with the strongest brand. It's the one that can prove fit across security, response, and compliance.
Use this as your screening sequence
- Technical capability: Confirm support for Microsoft 365 administration, identity governance, endpoint control, backup, and onsite escalation. If the provider only talks about ticketing and antivirus, it's too shallow.
- Security posture: Ask about Conditional Access hardening, privileged account control, telemetry, and how it detects identity abuse. For more depth on vendor risk and data protection practices, protect client data with Ares is a solid external reference.
- Pricing transparency: Demand a clear statement of what's included in the monthly fee, what triggers extra charges, and how urgent incidents are handled.
- SLA commitments: Look for documented response commitments, not verbal promises.
- Regional serviceability: Verify whether the provider can support your city with local technicians or dependable onsite reach. Don't assume a Toronto or Edmonton brand automatically serves Prairie markets well.
- Compliance readiness: Confirm awareness of PIPEDA, provincial privacy expectations, and audit support for your sector.
- Cultural fit: Your internal team needs a provider that communicates clearly and escalates without drama.
Red flags are easy to spot if you stay disciplined. Avoid vendors that won't name their escalation process, bury response times in fine print, or treat identity governance as an advanced extra rather than a standard requirement. In 2026, those gaps are not minor, they're the exact places where operational risk enters the business.
Secure Your Corporate Identity and Infrastructure
Canadian SMBs do not fail security reviews because of a missing antivirus alert. They fail because identity controls are weak, access is too broad, and nobody has a clear view of who can reach what. If you are serious about securing financial data as a small business, start with identity, device control, and the systems that move money and sensitive records. A proactive review of corporate identity and infrastructure is the right move, and the Identity Security Assessment Framework gives you a practical place to begin.
Regional serviceability matters just as much. Prairie and Western Canadian SMBs need an MSP that can respond locally, explain its escalation path, and prove it can handle onsite issues without relying on vague promises from a Toronto office. If the provider cannot show how it secures Microsoft 365, controls privileged accounts, and spots identity abuse, the rest of the stack is secondary.
Accelerate IT Services Inc. helps Canadian SMBs secure identities, harden Microsoft 365, and keep operations stable with managed support built around local response and fixed monthly pricing. If you are comparing managed IT providers in Canada, visit Accelerate IT Services Inc. to see how a security-first model can fit your environment and reduce avoidable downtime.


